

2021 and 2022 were the worst years on record for DeFi security, with a wave of bridge exploits, flash loan attacks and access-control failures that, combined, cost projects and users billions of dollars. The list below is still the clearest teaching material we have: every entry is a real, documented failure mode that a proper smart contract audit is specifically designed to catch. Every figure below is checked against rekt.news' incident database rather than repeated from the original reporting.
The 17 Biggest DeFi Hacks of 2021–2022, Ranked
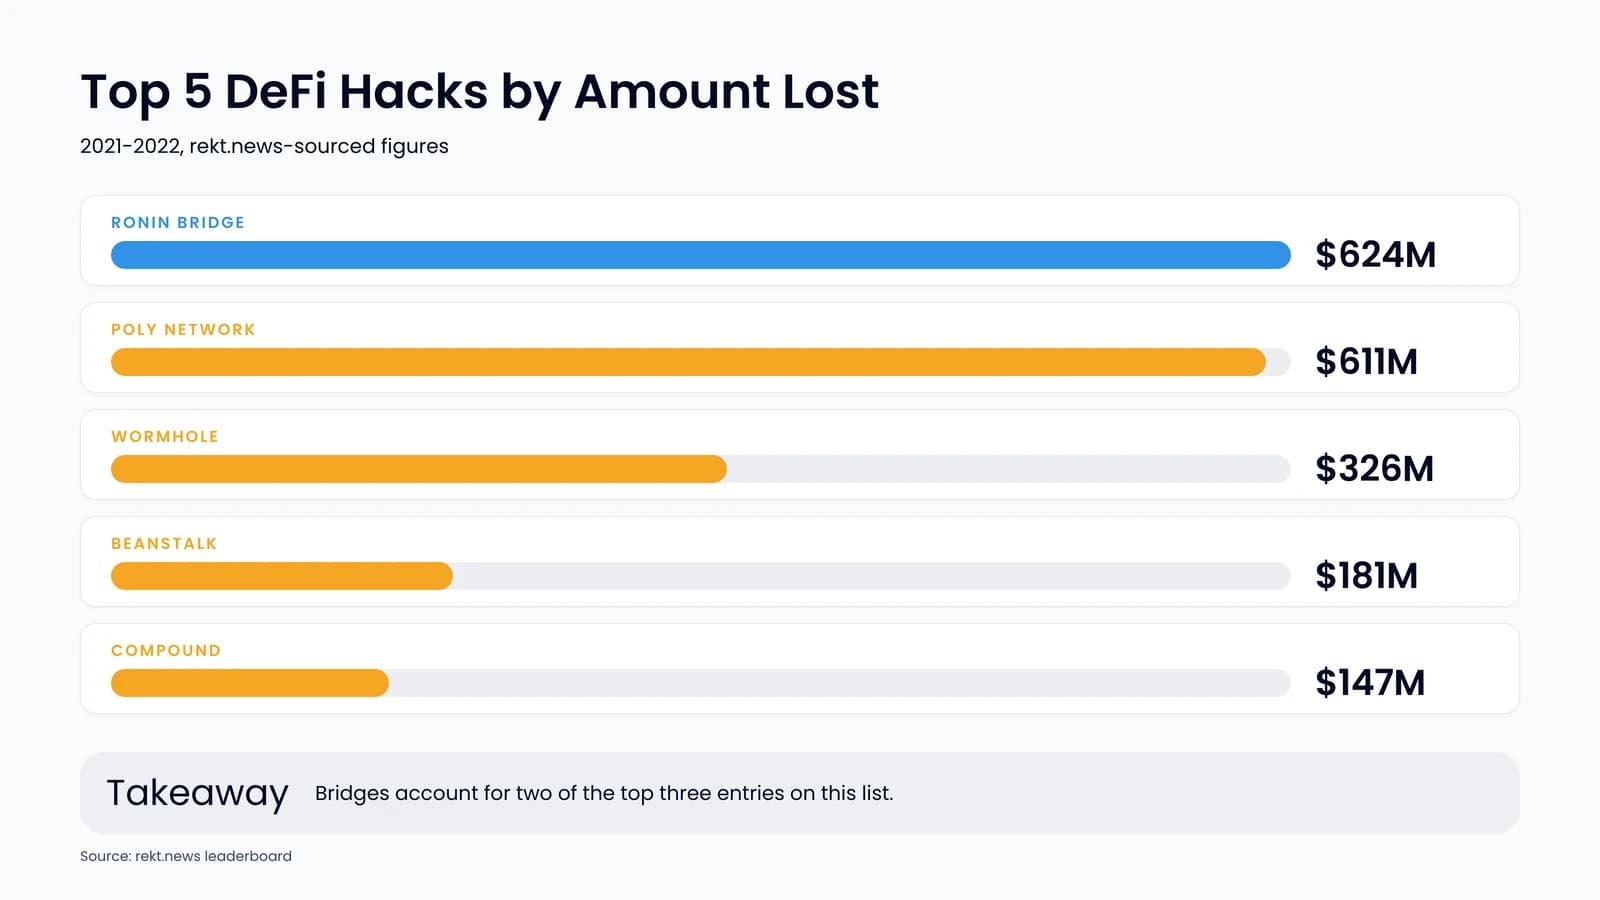
Ranked by amount lost, largest first.
1. Ronin Bridge: $624 Million
Date: March 23, 2022 (discovered ~6 days later). Type: private key compromise.
Attackers compromised five of the nine validator keys securing the Ronin bridge (used by the NFT game Axie Infinity to move funds between Ethereum and Ronin) and forged withdrawals for 173,600 ETH and 25.5 million USDC. The FBI later attributed the attack to North Korea's Lazarus Group. It remains one of the two largest crypto hacks ever recorded.
2. Poly Network: $611 Million
Date: August 10, 2021. Type: exploit (cross-chain contract logic flaw).
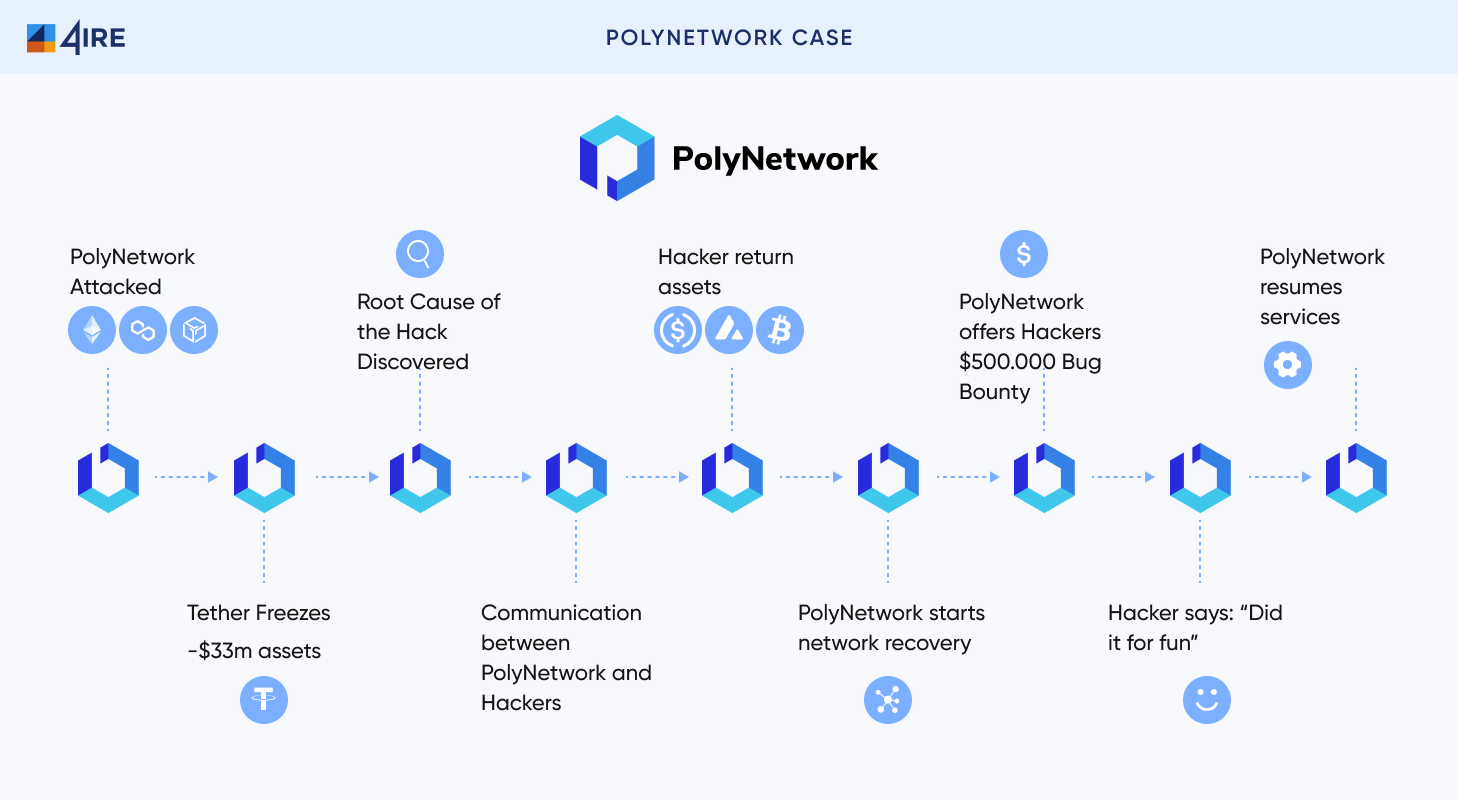
The attacker exploited a flaw in how Poly Network's contracts verified cross-chain messages across Ethereum, BNB Chain and Polygon, redirecting assets to their own addresses. In an unusual ending, the hacker returned nearly all the funds within days and was offered, and declined, a position as Poly Network's chief security advisor.
3. Wormhole: $326 Million
Date: February 2, 2022. Type: exploit (signature verification bypass).
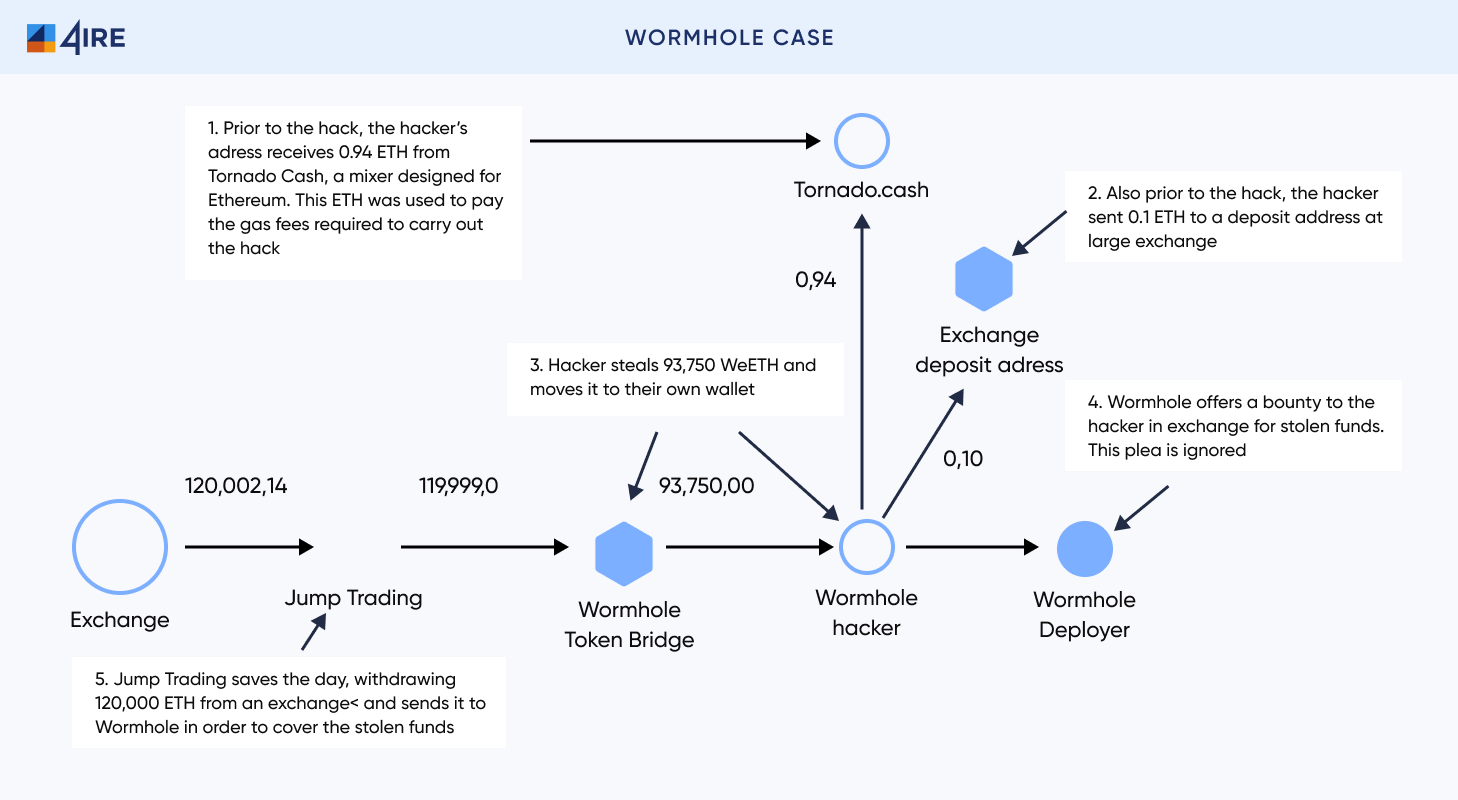
An attacker forged a validator signature on the Wormhole bridge, minting 120,000 wrapped ETH on Solana without depositing the real ETH backing it. Jump Crypto, Wormhole's backer, replaced the missing ETH within a day to keep the bridge solvent.
4. Beanstalk: $181 Million
Date: April 17, 2022. Type: flash loan governance attack.
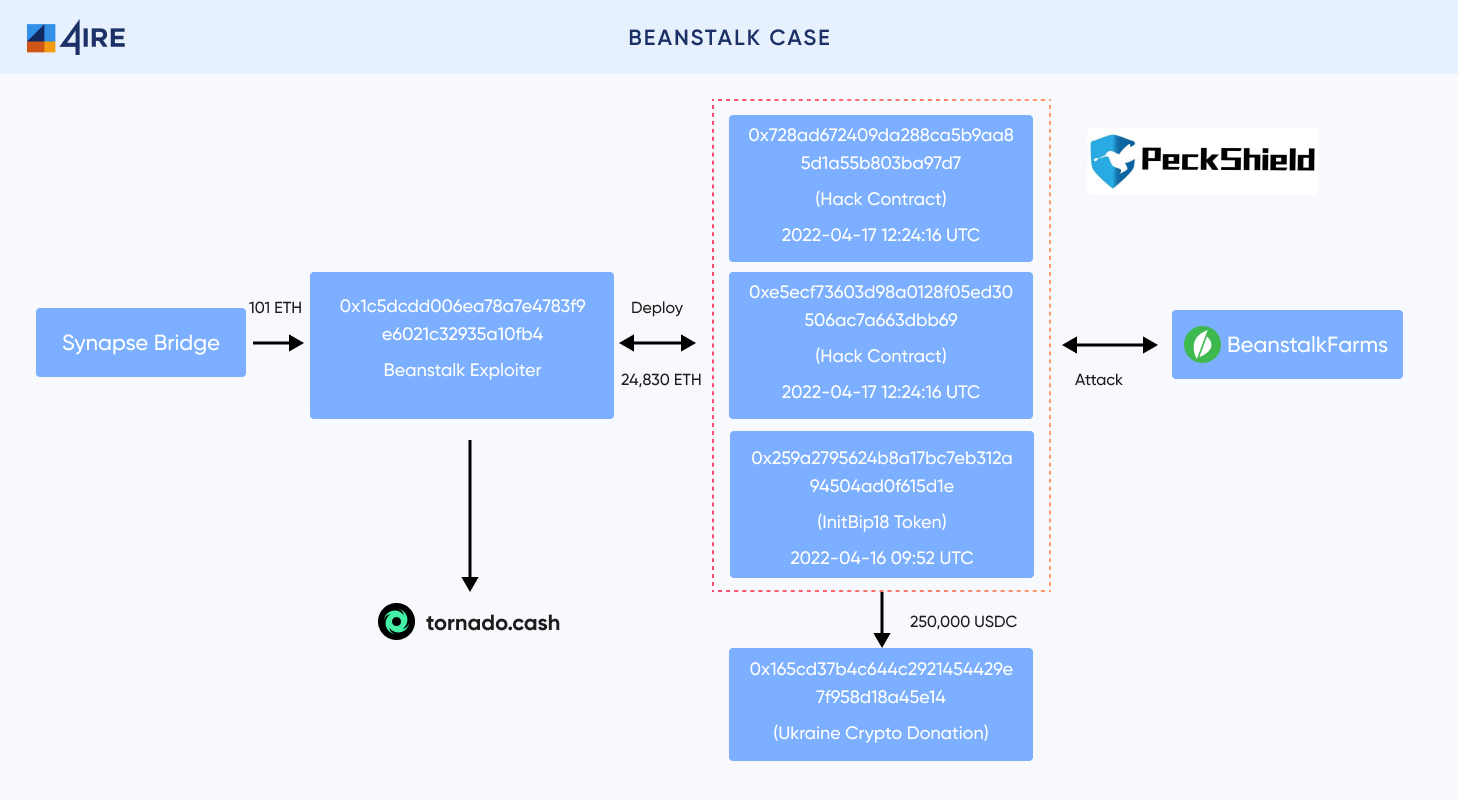
The attacker used a flash loan to briefly acquire enough governance weight to pass a malicious proposal in the same transaction, draining the protocol's treasury. It remains one of the largest flash loan attacks on record and a textbook case for why governance proposals need a timelock, not just a vote.
5. Compound: $147 Million
Date: September 29, 2021. Type: access control / distribution bug.
A flawed contract upgrade let users claim far more COMP governance tokens than they were entitled to. Because the bug was in a live, immutable contract, the team could not simply patch it, so a community vote was needed to authorize a fix, and a meaningful share of the excess tokens was voluntarily returned by community members.
6. Vulcan Forged: $140 Million
Date: December 13, 2021. Type: private key theft.
Attackers stole private keys for 96 wallets on the crypto-gaming platform and drained roughly 4.5 million PYR tokens along with other assets, a reminder that key management, not just contract logic, is part of an audit's scope.
7. Cream Finance: $130 Million
Date: October 27, 2021. Type: flash loan / price oracle exploit.
This was Cream Finance's third major exploit within the year (after smaller incidents in February and August 2021), using a flash loan to manipulate the exchange rate used by its Iron Bank lending market.
8. Badger DAO: $120 Million
Date: December 2, 2021. Type: front-end compromise.
Attackers injected malicious code through a compromised Cloudflare API key, inserting a script into Badger's front end that tricked users into approving withdrawals to the attacker's address. The underlying smart contracts were never touched. The vulnerability was in the web front end.
9. Horizon Bridge (Harmony): $100 Million
Date: June 23, 2022. Type: private key compromise.
Attackers obtained enough private keys to approve fraudulent transactions on Harmony's Horizon bridge, which used a 2-of-5 multisig, a low threshold for a bridge holding that much value. US authorities later attributed the attack to North Korea's Lazarus Group.
10. Qubit Finance: $80 Million
Date: January 27, 2022. Type: exploit (bridge logic flaw).
The attacker tricked Qubit's QBridge contract into recognizing a deposit that was never actually made, then withdrew real assets against it on BNB Chain.
11. Rari Capital / Fei Protocol Fuse: $80 Million
Date: April 30, 2022. Type: reentrancy.
A reentrancy bug in Rari's Fuse lending pools let the attacker drain multiple pools in a single attack. Rari (merged with Fei Protocol in late 2021) offered a $10 million bounty for the return of funds; Fei Protocol shut down a few months later, partly as a result.
12. bZx: $55 Million
Date: November 5, 2021. Type: private key compromise.
A bZx team member's private key was compromised, letting the attacker mint and withdraw funds directly, a different and much larger incident than bZx's earlier, smaller 2020 price-oracle exploits.
13. PancakeBunny: $45 Million
Date: May 19, 2021. Type: flash loan / price manipulation.
The attacker used a flash loan to distort the USDT/BNB and BUNNY/BNB pool prices, then minted a large volume of BUNNY tokens against the inflated price before dumping them, crashing BUNNY's price and the protocol's total value.
14. Vee Finance: $34 Million
Date: September 21, 2021. Type: oracle manipulation.
Vee Finance's leveraged trading relied on a single price oracle (Pangolin). The attacker created new trading pairs and manipulated prices on that one source, bypassing slippage checks to open positions at distorted prices.
15. Meerkat Finance: $31 Million
Date: March 4, 2021. Type: disputed (exploit or insider action).
One day after launch, roughly 73,000 BNB and $14 million in BUSD left Meerkat's vaults through a privileged admin function. The team called it a hack, but trackers including DefiLlama classify it as a rug pull, given the timing one day post-launch and the use of privileged access rather than an external exploit.
16. Grim Finance: $30 Million
Date: December 18, 2021. Type: reentrancy.
A reentrancy bug let the attacker feed fake deposits into Grim Finance's yield vaults while earlier deposits were still processing. A prior audit had flagged the contract's reentrancy guard as active when it was not.
17. OpenSea (Wyvern Protocol): $1.7 Million
Date: February 19, 2022. Type: phishing / order-matching bug in the NFT marketplace's underlying Wyvern protocol.
A phishing email disguised as an OpenSea contract-migration notice tricked users into signing a blind order that matched their own still-active, below-market Wyvern listings, letting the attacker buy their NFTs at those old prices. Initial reports put the number of affected users at 32; OpenSea later confirmed 17 users had assets taken. It is the smallest amount on this list by two orders of magnitude, and it still cost real collectors real money.
What These Hacks Have in Common
- Bridges are still the single riskiest component. Ronin, Wormhole, Horizon and Qubit (four of the five largest entries here) were all cross-chain bridges, and bridge security has remained one of the hardest problems in the space since.
- Private keys and operational security matter as much as contract logic. bZx, Vulcan Forged and Horizon were all key-compromise incidents, not code bugs. No smart contract audit catches a stolen key, which is why key management and multisig thresholds need their own review.
- Flash loans turn a single transaction into a powerful attack tool. Beanstalk, PancakeBunny, Cream Finance and Vee Finance all used a flash loan to manipulate price or governance state within one atomic transaction. This remains one of the first attack patterns any DeFi audit tests for.
- An audit report from before launch is not a permanent guarantee. Grim Finance shipped with an audit that had (incorrectly) marked its reentrancy guard as active. Re-auditing after any material change, and treating an audit as a snapshot rather than a certificate, would have caught it.
How to Reduce Your Own Exposure
- A pre-launch smart contract audit from a firm with real track record and manual review, not automated scanning alone. See our guide to auditing smart contracts for what that process should look like.
- Re-audit after every material change, not just at launch: several hacks on this list happened well after initial deployment, following an upgrade or a new integration.
- Multiple independent price sources for anything a contract prices on-chain; a single oracle is a single point of failure.
- Multisig with a real threshold and a timelock on anything that can move significant funds, including DAO treasury contracts.
- Operational security for keys and infrastructure (API keys, CI/CD, admin credentials) treated with the same seriousness as the contract code. Badger DAO and bZx were both compromised outside the contract layer entirely.
How 4IRE Can Help
4IRE audits and builds smart contracts for DeFi, DAO and tokenization projects. If you're approaching a launch, talk to us about scoping a security review before your project ends up as a case study on a list like this one.
Don't Become the Next Case Study
Our team audits and builds smart contracts for DeFi, DAO and tokenization projects. Schedule a free consultation before your next launch.
FAQ
The Ronin Bridge hack in March 2022, at roughly $624 million (173,600 ETH and 25.5 million USDC), attributed by the FBI to North Korea's Lazarus Group. Poly Network's $611 million exploit in August 2021 is a close second.
No. A proper audit is specifically designed to catch reentrancy, oracle manipulation, flash loan attacks and governance-logic flaws — several entries on this list. But private-key theft (bZx, Vulcan Forged, Horizon) and front-end compromises (Badger DAO) happen outside a smart contract's code and need separate operational security and key-management controls.
Yes. Grim Finance was exploited despite an existing audit report, because that report had incorrectly marked a security control as active. Any material code change, new integration, or upgrade should trigger a fresh review rather than relying on the original audit indefinitely.
Bridges hold large pooled balances of assets and depend on trusting a limited set of validators or a signature scheme to authorize withdrawals on the destination chain. That combination — a large treasury plus a relatively small trust set — has made bridges the single most exploited category of DeFi infrastructure, as four of the five largest hacks on this list show.