

 DeFi

Most DeFi teams are strong on product and weak on the language-specific pitfalls of smart contract development. That gap shows up in the code, and in DeFi a single overlooked bug can drain user funds in one transaction and end the project's reputation with it. That is why a smart contract audit before mainnet launch has become standard practice rather than an optional extra.
What a Smart Contract Audit Actually Checks
An audit is an independent, line-by-line review of your contract code before it goes live and becomes effectively unchangeable. It looks for three different classes of problem:
- Security vulnerabilities: bugs that let an attacker drain funds, mint tokens they shouldn't, or take over admin functions.
- Logic errors: places where the code does not match the whitepaper or spec, so the contract executes the wrong behavior even without an attacker involved.
- Gas inefficiency: code that costs users more than it needs to on every transaction.
A concrete example: if a contract's admin role can change withdrawal parameters or pull user funds without a timelock or multisig, that is a design flaw an audit is built to catch, the kind of thing that looks fine in a demo and becomes a headline later.
How a Smart Contract Audit Is Performed
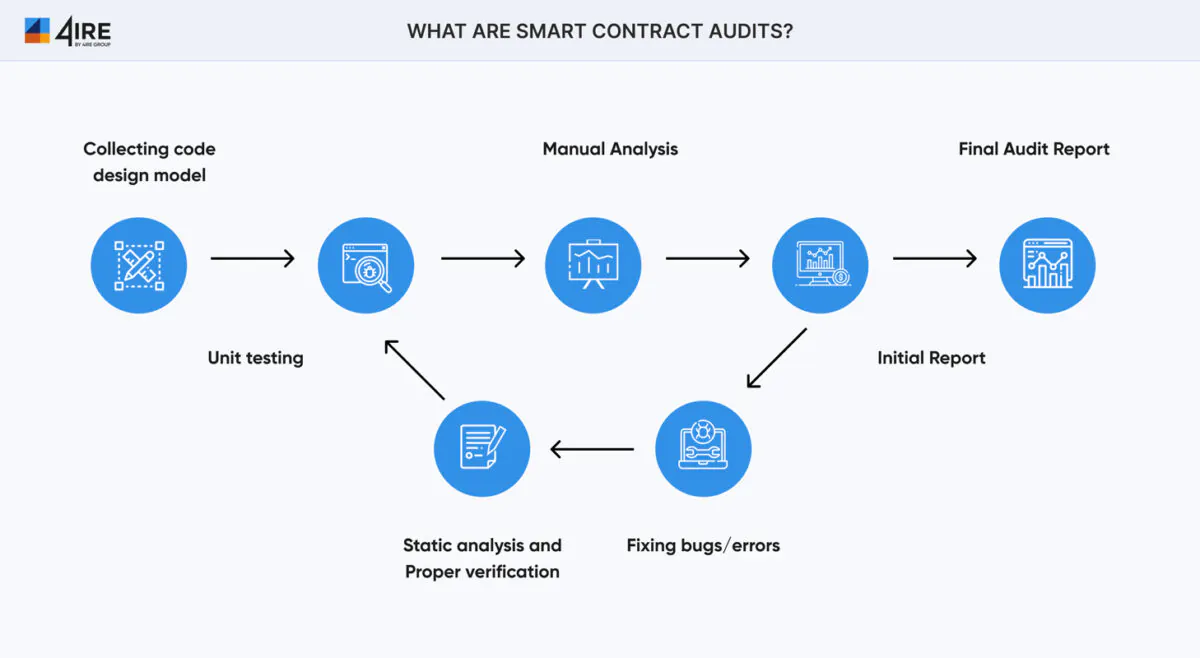
| Stage | What happens |
|---|---|
| Requirement gathering | The auditor collects the whitepaper, technical spec and repository access to understand intended behavior before reading code. |
| Automated analysis | Static-analysis and symbolic-execution tools flag common vulnerability patterns quickly, narrowing where manual review needs to focus. |
| Manual review | Senior auditors read the code line by line for business-logic errors, edge cases and issues automated tools cannot reason about. |
| Testing | Unit tests, fuzzing and testnet deployment confirm the contract behaves as specified under both normal and adversarial inputs. |
| Initial report | Findings are ranked by severity with proof-of-concept and remediation guidance for each. |
| Remediation and re-audit | The team fixes the issues; the auditor verifies the fixes and checks that nothing new was introduced. |
| Final report | A public or client-facing report documents what was found, what was fixed, and any accepted residual risk. |
Types of Smart Contracts That Need an Audit
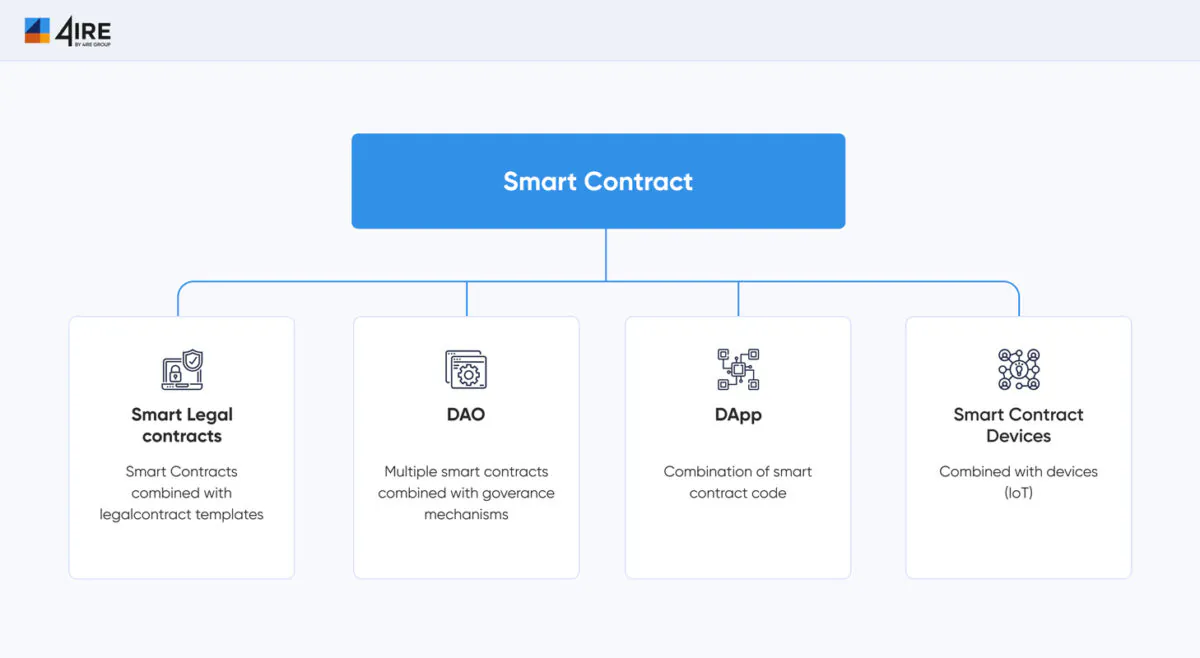
- DAO governance contracts. These control a shared treasury and execute the outcome of votes automatically, so an admin-key or logic bug is a direct route to the treasury. See our DAO development cost guide for the governance stack this usually involves.
- Smart legal contracts, which self-execute contractual obligations once conditions are met, replacing manual enforcement.
- DApp contracts powering lending, trading or payment logic, where the contract IS the product.
- IoT / applied-logic contracts that trigger automatically from device data, common in supply-chain and asset-tracking use cases.
What You Need to Prepare for an Audit
A frozen, feature-complete version of the code and a detailed whitepaper or technical spec are the two things an auditor needs to do a thorough job. Auditing a moving target wastes the auditor's time on your budget. Freeze the code first, then run some of the basic checks yourself (compiler warnings, obvious reordering or replay issues) so the auditor can spend their time on what actually needs expert eyes.
How to Choose an Auditor
- Check their track record. Look at contracts they have already audited, and check whether any of those projects were exploited afterward, and how the firm responded.
- Do your own due diligence. Talk to their auditors directly, ask for case studies, and ask what tools and methodology they actually use.
- Consider more than one audit for anything holding significant value. A second independent review can catch what the first one missed; consensus across multiple audits is a real signal in a space where no single audit is a guarantee.
4IRE's own smart contract audit engagements typically run $5,000–$15,000 for a standard contract, with turnaround from 24–48 hours to a couple of weeks; a full DeFi protocol or cross-chain bridge re-audit can run $40,000–$90,000 and take 4–8 weeks, per our own how-to-build-an-AMM cost breakdown.
Where Smart Contracts Get Used
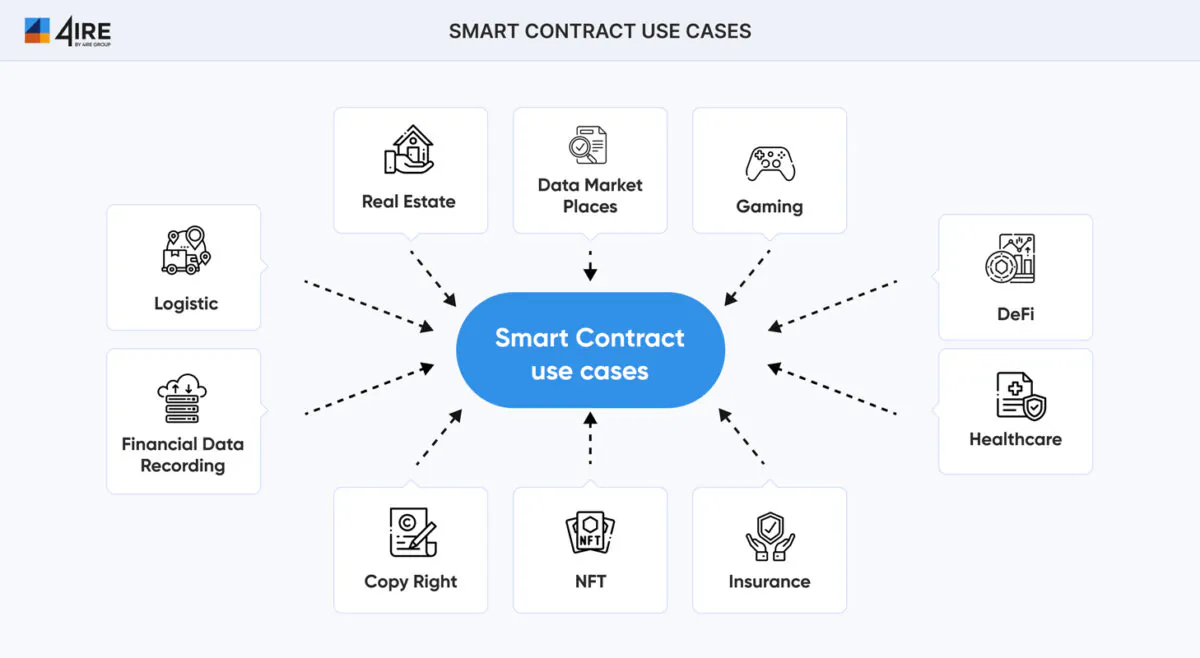
- Financial services: lending, trading and payments without a third-party intermediary taking a cut.
- Digital identity: transparent yet privacy-preserving KYC and access control.
- Business operations: invoicing, inventory and counterparty transactions automated end to end.
- Real estate: transparent ownership history and, through real world asset tokenization, fractional access for smaller investors.
- Supply chain: provenance tracking that end customers can verify themselves.
- Gaming and NFTs: ownership, trading and cross-chain movement of in-game assets.
- Marketplaces: exchanges and NFT marketplaces where the contract enforces the trade terms.
An Audit Is Not a Guarantee
An audit dramatically lowers risk; it does not eliminate it. It is a snapshot review of a specific code version at a specific point in time. It cannot catch a zero-day vulnerability class nobody has seen yet, and it says nothing about risk introduced later by an upgrade, a dependency, or an oracle you integrate afterward. Treat an audit as a required gate before launch, not a permanent safety certificate, and re-audit after any material change to the code.
How 4IRE Can Help
4IRE audits smart contracts across DeFi, tokenization and gaming projects, and builds the contracts themselves through our DeFi development team. If you're approaching launch, talk to us about scoping an audit before you deploy. It is far cheaper before an incident than after one.
Ready for a Smart Contract Audit?
Tell us about your contract and timeline, and we'll scope an audit that fits before you deploy. Schedule a free consultation with our experts.
FAQ
Turnaround depends on complexity: a simple, standalone ERC-20 contract can be audited in a few days, while a large DeFi protocol with multiple interconnected contracts can take several weeks. Plan the audit into your launch timeline rather than treating it as a final rush step.
4IRE's smart contract audits typically run $5,000–$15,000 for a standard contract; a full DeFi protocol or cross-chain bridge re-audit can run $40,000–$90,000, with a longer 4–8 week timeline to match the larger attack surface.
Only if it was designed to be upgradeable, or if it has not been deployed yet. A non-upgradeable contract already live on mainnet cannot be patched: issues found after launch require a new deployment or a governance-approved migration, which is exactly why the audit needs to happen before launch, not after.
No. An audit is a thorough, expert review of a specific code version at a point in time, and it substantially lowers risk, but it cannot catch every possible future exploit class or risk introduced by later changes, integrations or oracle dependencies. Treat it as a required gate, not a permanent guarantee.