

 Blockchain news

A smart contract audit is a security-focused code review performed before a contract goes live: once deployed, most contracts cannot be patched, so vulnerabilities found after launch are far more expensive than the ones caught before it. As blockchain adoption keeps growing, an independent audit has become the baseline expectation for any project holding user funds, not a nice-to-have.
This guide, from the 4IRE team, covers what auditors actually look for, the vulnerability classes that come up again and again, manual vs. automated methods, and realistic 2026 cost and timeline expectations for a smart contract audit.
What Is a Smart Contract Audit?
An audit is best understood as a code review performed by someone who did not write the code, which matters, because a contract's own author is the person least likely to catch their own blind spots. Once a contract is deployed and immutable, there is no patch Tuesday; the review has to happen before launch.
The results matter beyond security. A public audit report is one of the clearest trust signals you can give users and investors, particularly for anything involving asset tokenization or real user deposits.
The Vulnerability Classes an Audit Looks For
- Reentrancy. A malicious contract calls back into the vulnerable contract before its first call finishes, draining funds through repeated withdrawals. This is the pattern behind The DAO hack and remains one of the most-checked issues in any audit.
- Timestamp dependence. Contracts that rely on block.timestamp for critical logic (betting deadlines, unlock times) can be manipulated within the small window miners/validators control.
- Cross-function race conditions. Two functions sharing state can be called in an interleaved order that lets an attacker act on stale state, classically by calling withdraw again before a balance update lands.
- Integer overflow/underflow. Largely mitigated in modern Solidity (built-in overflow checks since 0.8.0), but still a real risk in older codebases, other languages, or unchecked math blocks.
- Gas limit and unbounded loops. A loop over an unbounded array can exceed the block gas limit and permanently brick a function once the underlying list grows large enough.
- Unchecked external calls. Failing to check the return value of an external call, or trusting an untrusted contract's callback, opens the door to unexpected control flow.
- Front-running. Public mempools let anyone see a pending transaction and submit their own ahead of it, a real problem for DeFi apps without commit-reveal or private mempool protections.
- Oracle and price manipulation. Relying on a single, thinly-traded price source lets an attacker distort the price within one transaction and drain a lending or AMM contract against it.
Manual vs. Automated Auditing
Neither method alone is sufficient. Automated static analysis and fuzzing tools scan quickly and catch known vulnerability patterns cheaply, which is why every serious audit starts there. It clears the obvious issues fast and lets human reviewers focus their time on what tools cannot reason about: business logic, economic incentives, and how contracts interact under adversarial conditions. A manual review by an experienced auditor is what catches the issues that make headlines; automated tools alone consistently produce both false positives and false negatives.
Tools Commonly Used in Smart Contract Audits
- Slither. A widely used open-source static analyzer for Solidity from Trail of Bits; fast, and the standard first pass in most audit workflows.
- Mythril. An open-source symbolic execution tool that explores contract execution paths to find deeper logic and security issues than simple pattern matching. (MythX, the hosted commercial service built on it, was sunset by ConsenSys Diligence in 2023, so use Mythril directly, or Diligence Fuzzing as its successor.)Symbolic execution tools that explore contract execution paths to find deeper logic and security issues than simple pattern matching.
- Echidna and Foundry-based fuzzing. Property-based fuzzers that throw large volumes of randomized input at a contract to find edge cases a human reviewer would not think to test manually.
- Solhint. A Solidity linter that catches style and common-mistake issues before the code even reaches an auditor.
Tooling changes fast in this space, and a good audit firm's toolchain evolves with it, so treat any specific tool list, including this one, as a snapshot rather than a permanent standard.
How the Audit Process Works
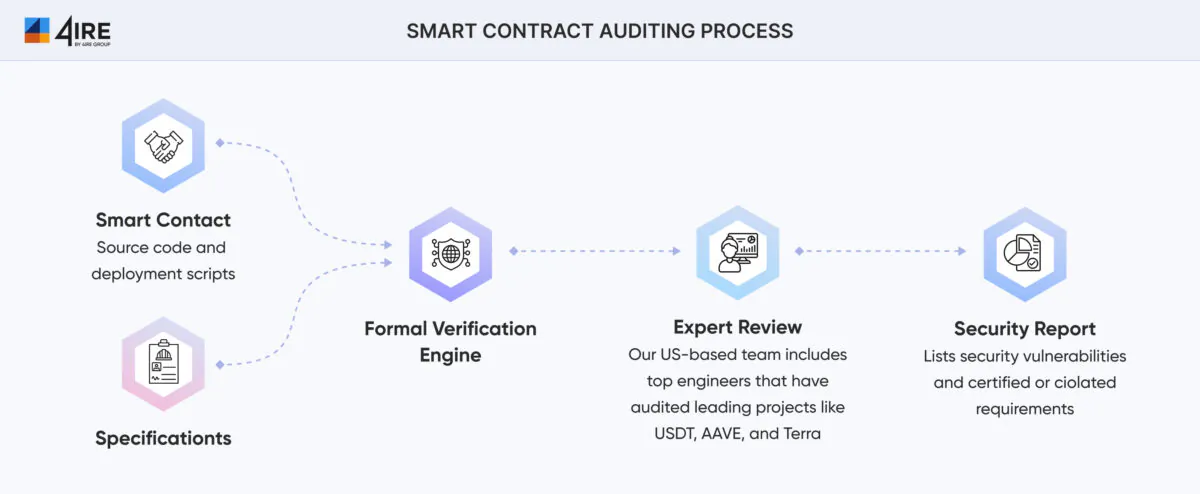
- Freeze the code. Auditing a moving target wastes budget; lock the version being reviewed.
- Automated pass. Static analysis and fuzzing tools run first to clear common issues quickly.
- Manual review. Senior auditors read the code line by line, verify gas usage and documented behavior, and test the architecture against the intended design.
- Report and remediation. Findings are ranked by severity with proof-of-concept and fix guidance; the team fixes them and the auditor verifies the fixes.
- Final report. A standard audit report will state it does not provide a legal security guarantee. That is a liability disclaimer, not a sign of a weak audit.
Things to Consider Before You Commit
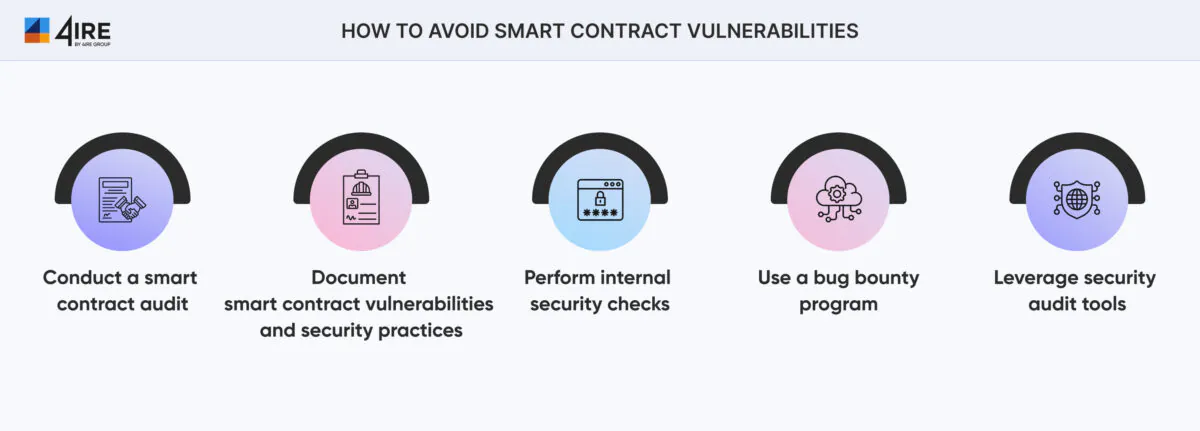
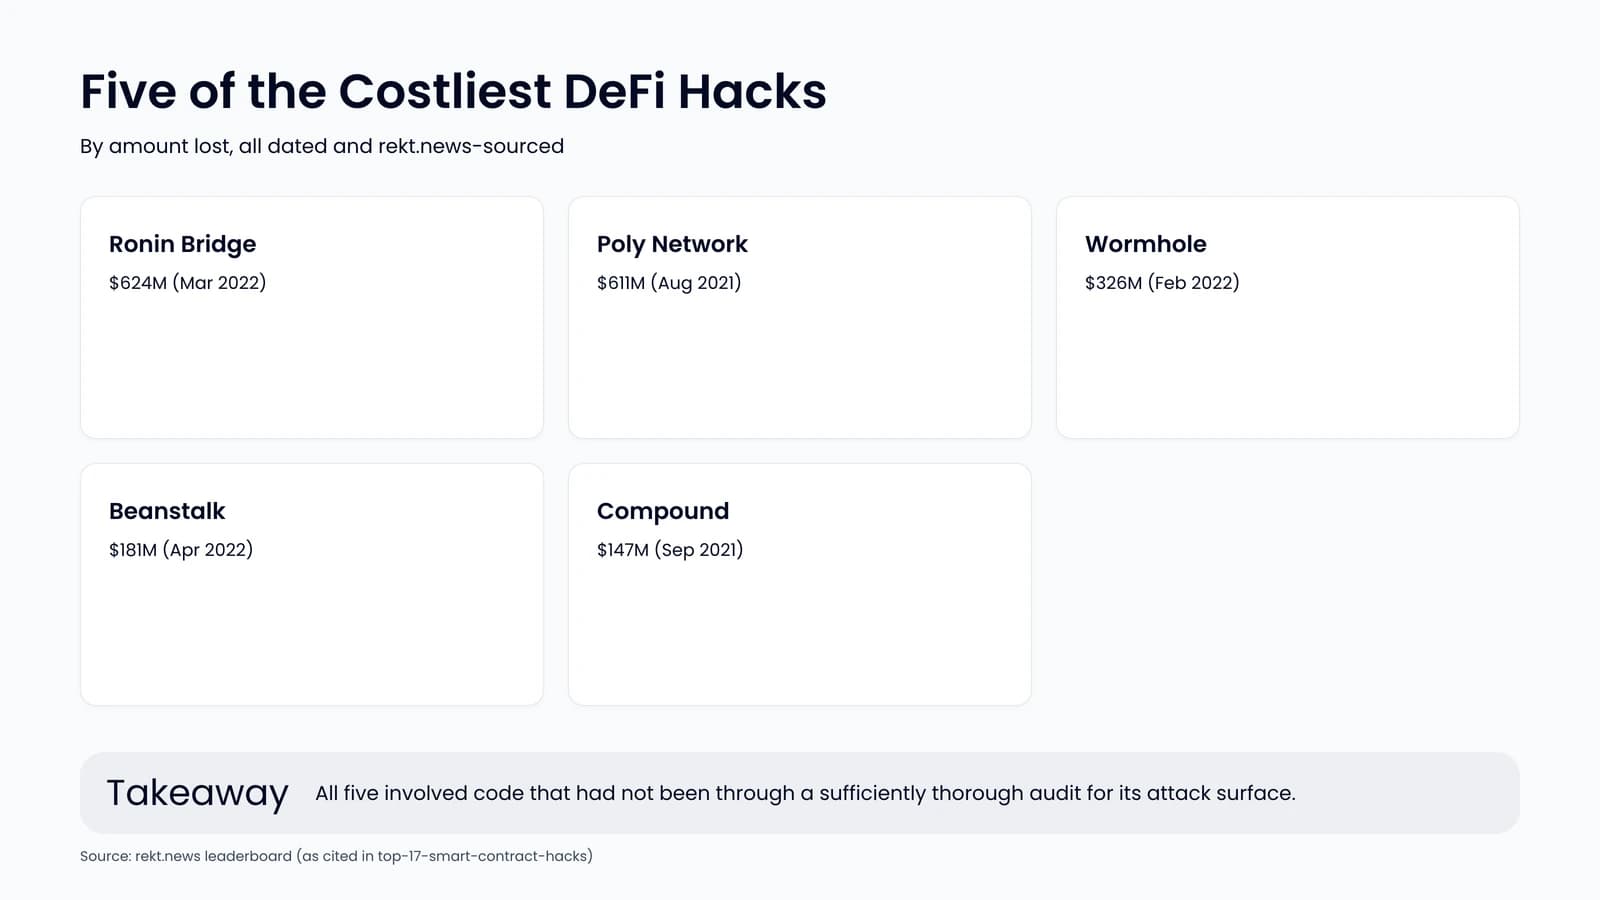
Not every self-described "audit" is equal. Some are rubber-stamp reviews performed quickly by inexperienced teams, and a badly audited project with a public "Audited" badge can be more dangerous than an honestly unaudited one, because it creates false confidence. This is exactly the failure mode behind several of the largest smart contract hacks on record: code that had supposedly been reviewed. Ask any prospective auditor for their track record, their methodology, and whether any of their previously audited projects were later exploited, and how they responded when that happened.
Governance and DAO Contracts Need the Same Scrutiny
Audits are not only for token and DeFi logic. A DAO's governance contracts control a shared treasury and execute automatically once a vote passes, which makes them just as attractive a target as any lending pool, and a DEX or AMM carries its own distinct surface (price oracles, liquidity accounting) that a generic audit checklist can miss if the auditor has not worked on that contract type before. Match the auditor's experience to your contract type, not just their general reputation.
How Long Does It Take?
A simple, standalone contract typically takes 24–48 hours to a week or two; a large, interconnected DeFi protocol or a cross-chain bridge can take 4–8 weeks. Build the audit into your launch timeline from the start rather than scheduling it as a final rush step before mainnet.
How Much Does It Cost?
4IRE's own smart contract audit engagements typically run $5,000–$15,000 for a standard contract; a full DeFi protocol or AMM-scale re-audit after implementation changes can run $40,000–$90,000, per our own how-to-build-an-AMM cost breakdown. Free or very cheap automated-only checks exist, but they are not a substitute for the manual review a real audit includes. Use them as a first pass, not a final answer.
Our Experience
4IRE provides smart contract audits as part of our broader blockchain consulting and DeFi work, combining automated tooling with senior manual review. If you want a second opinion on a contract someone else audited, or a first audit before launch, that is exactly the kind of engagement we scope regularly.
Final Thoughts
Auditing smart contracts is not a box to check before launch: it is the last real chance to catch a mistake before it becomes permanent and public. Budget for it from the start of the project, choose an auditor based on track record rather than price alone, and treat the audit report as a living document you revisit after every material change to the code.
Need a Smart Contract Audit?
Tell us about your contract and timeline, and our team will scope an audit that fits your launch date. Schedule a free consultation with our experts.
FAQ
Reentrancy, timestamp dependence, cross-function race conditions, unbounded loops that hit gas limits, unchecked external calls, front-running, and oracle/price manipulation are the classes that come up most often across real audits.
Immutability. Because a deployed, non-upgradeable contract cannot simply be patched, the review has to be thorough before launch: a missed issue becomes permanent and public rather than a quick fix. Reliance on external oracles for cross-chain or price data is the other recurring source of risk auditors focus on.
Look at their track record on comparable projects, ask whether any previously audited contracts were later exploited and how the firm responded, and confirm they combine automated tooling with real manual review rather than relying on automated scans alone.
4IRE's audits typically run $5,000–$15,000 for a standard contract, taking 24–48 hours to a couple of weeks; a large DeFi protocol or cross-chain bridge can run $40,000–$90,000 for a full re-audit and take 4–8 weeks.