

Every fintech founder eventually asks whether they need a license before launch. Most businesses that touch customer money do. The harder question is which license, and how early to start the process, because licensing timelines rarely match a product roadmap. In 2026, the map is also fuller than it was two years ago: MiCA is fully in force for crypto-asset service providers in the EU, the US has a federal framework for stablecoin issuers under the GENIUS Act, and EU firms increasingly have to plan for DORA's operational resilience rules on top of their core license.
This guide covers which activities actually trigger a license, the license types you're most likely to run into, what regulators check during an application, and how to think about timeline and cost. For a deeper comparison of license categories, see our overview of types of licenses for fintech and crypto.
What a License Actually Confirms
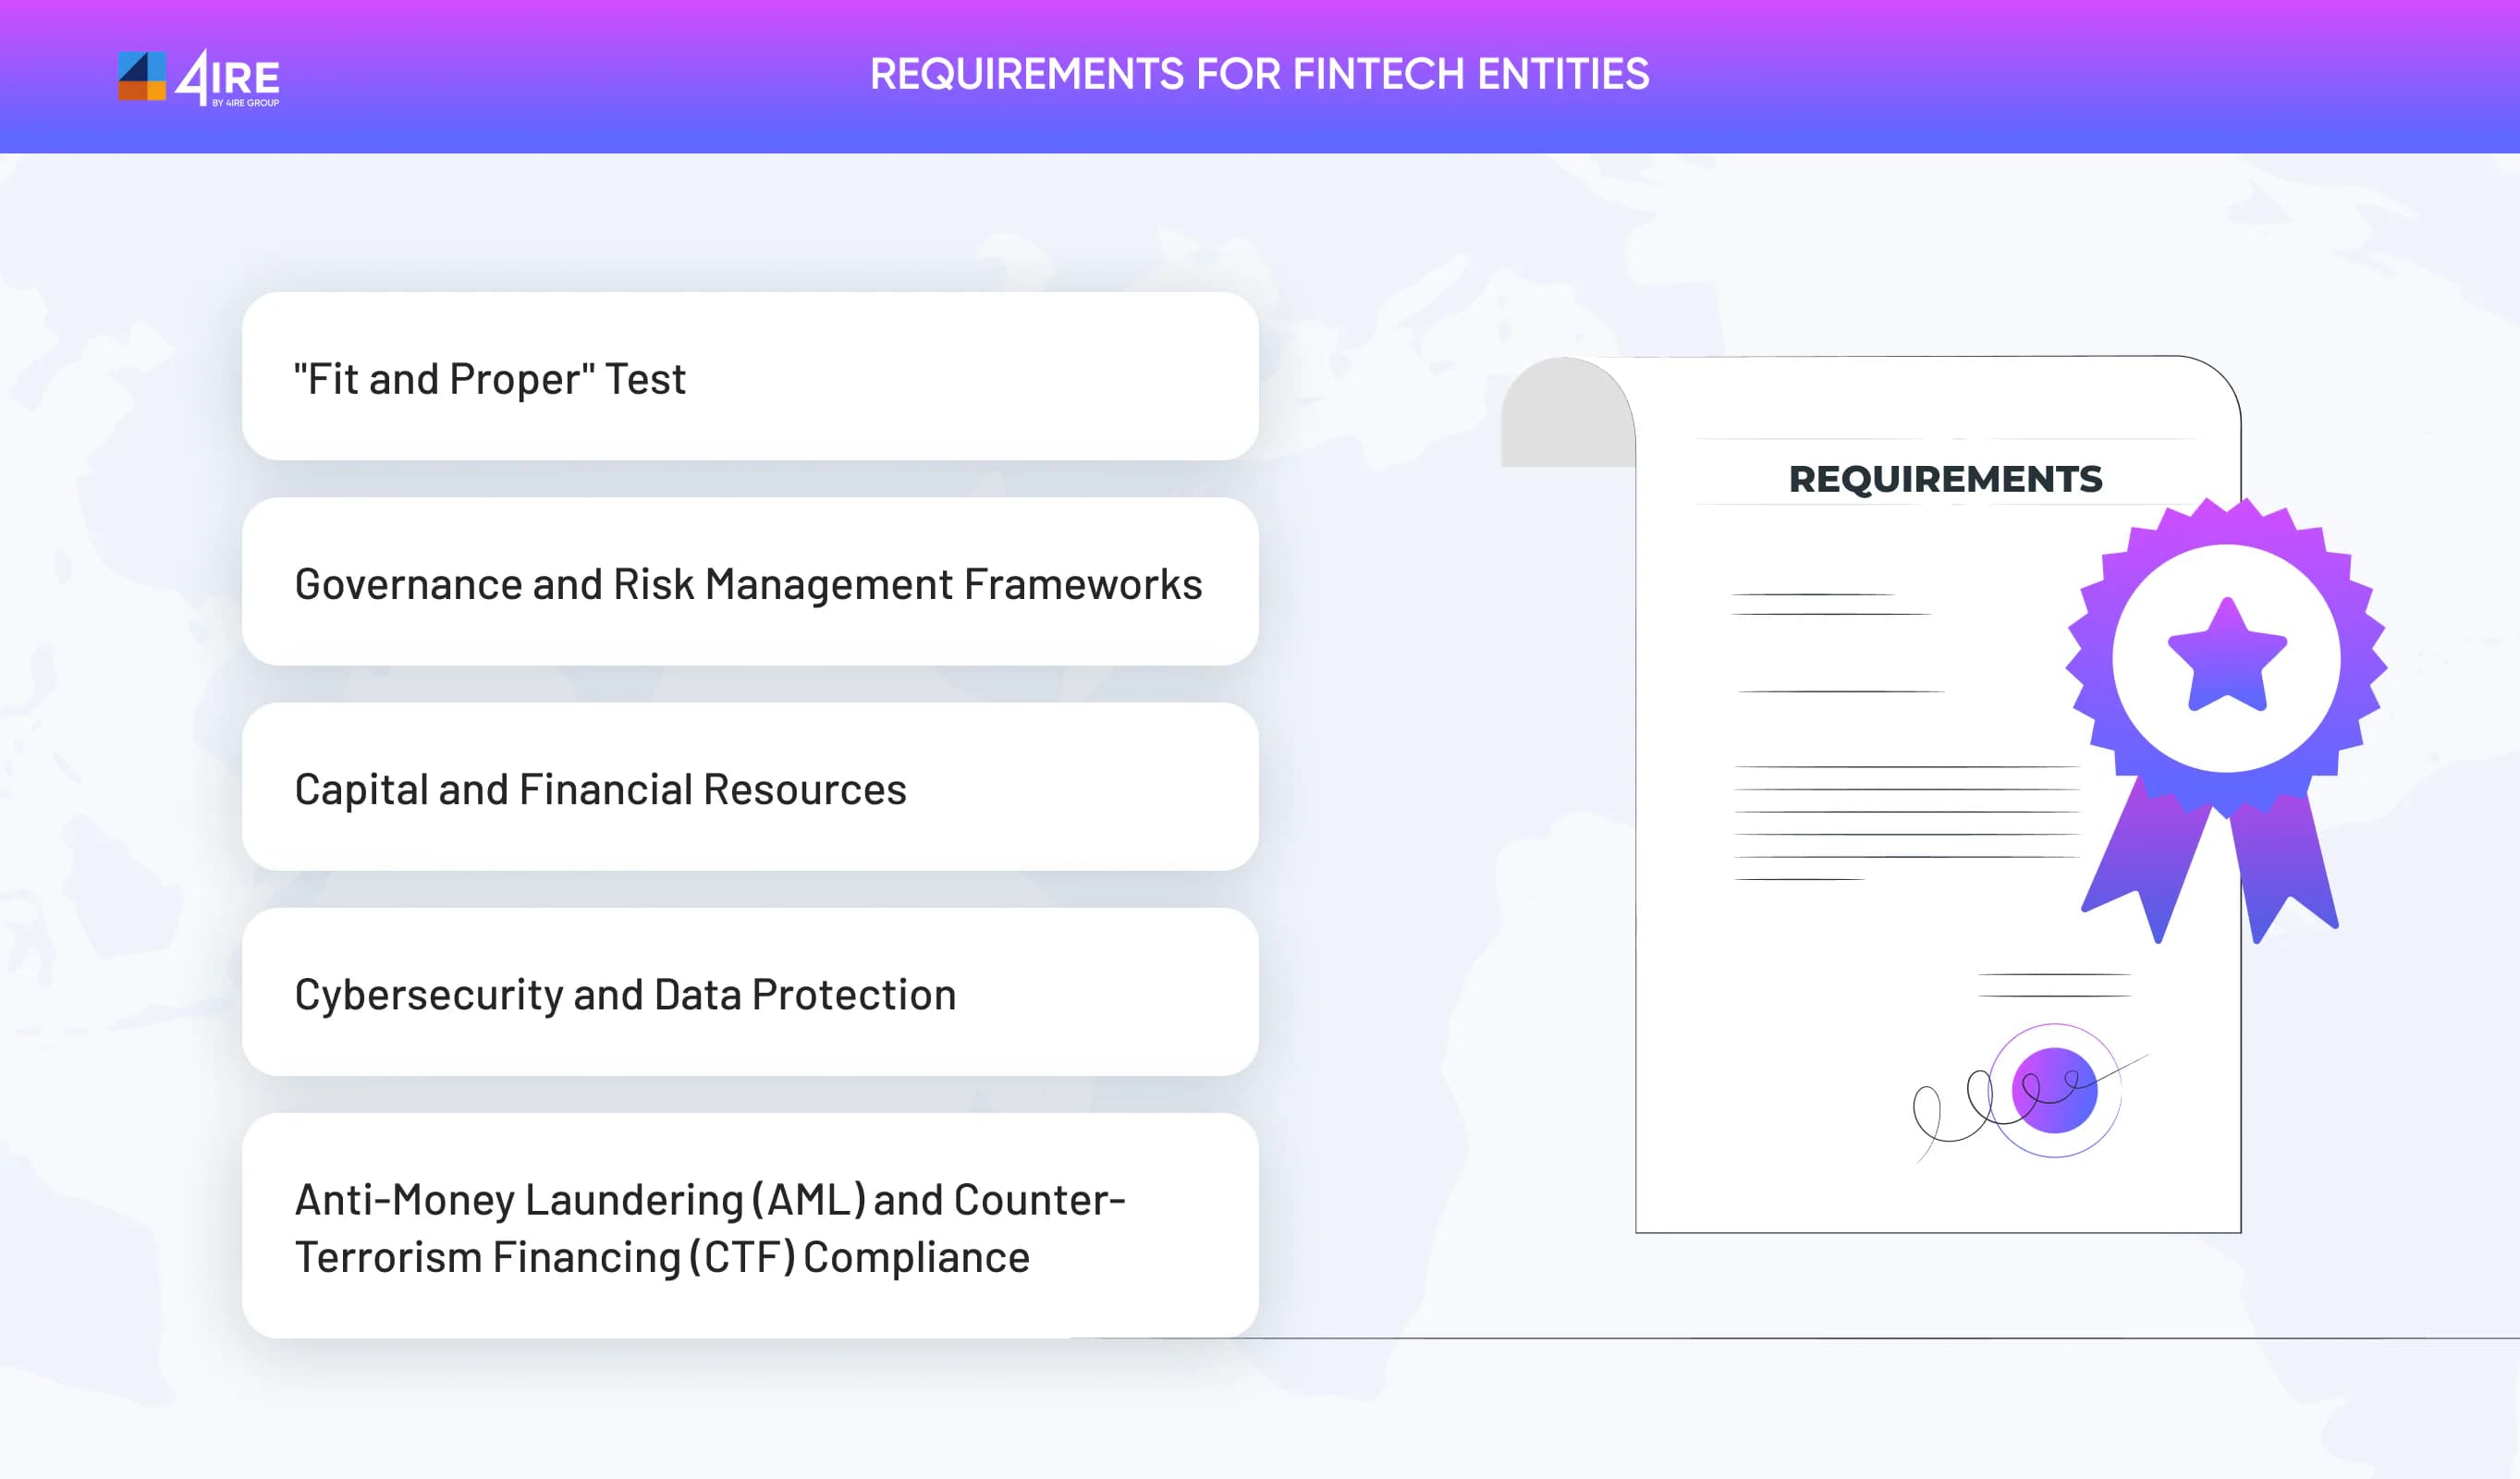
A license is not a formality. It's a regulator's confirmation that a business has enough capital to survive stress, internal controls it can demonstrate rather than describe, and concrete commitments to protect customer funds and data. Getting one means producing a real business plan, an AML/KYC program addressed to your actual customer base, and evidence of security controls, not a generic policy template. Regulators check whether the application matches operational reality, and they revisit that match after launch, not only at the start.
Which Activities Trigger a License
- Payment services and money transmission. Card issuance, money remittance, operating payment accounts, and acquiring card transactions generally need a payment service provider (PSP) license or, in the US, state money transmitter licenses.
- E-money issuance. Issuing prepaid balances or accounts that customers top up and spend from needs an electronic money institution (EMI) license in the EU and UK, or the equivalent money-transmitter authorization elsewhere.
- Crypto-asset services. Exchanging, custodying, or brokering crypto for clients needs a crypto-asset service provider (CASP) authorization under MiCA in the EU, state licenses or a federal charter in the US, and registration with the FCA for anti-money-laundering purposes in the UK.
- Issuing a payment stablecoin. In the EU this needs e-money-token issuer status under MiCA. In the US, the GENIUS Act creates a permitted payment stablecoin issuer status, though the implementing rules were not yet final as of September 2026.
- Consumer or business lending. Extending credit generally needs a consumer credit or lending license that is separate from, and additional to, any payments license.
The Main License Types You'll Encounter
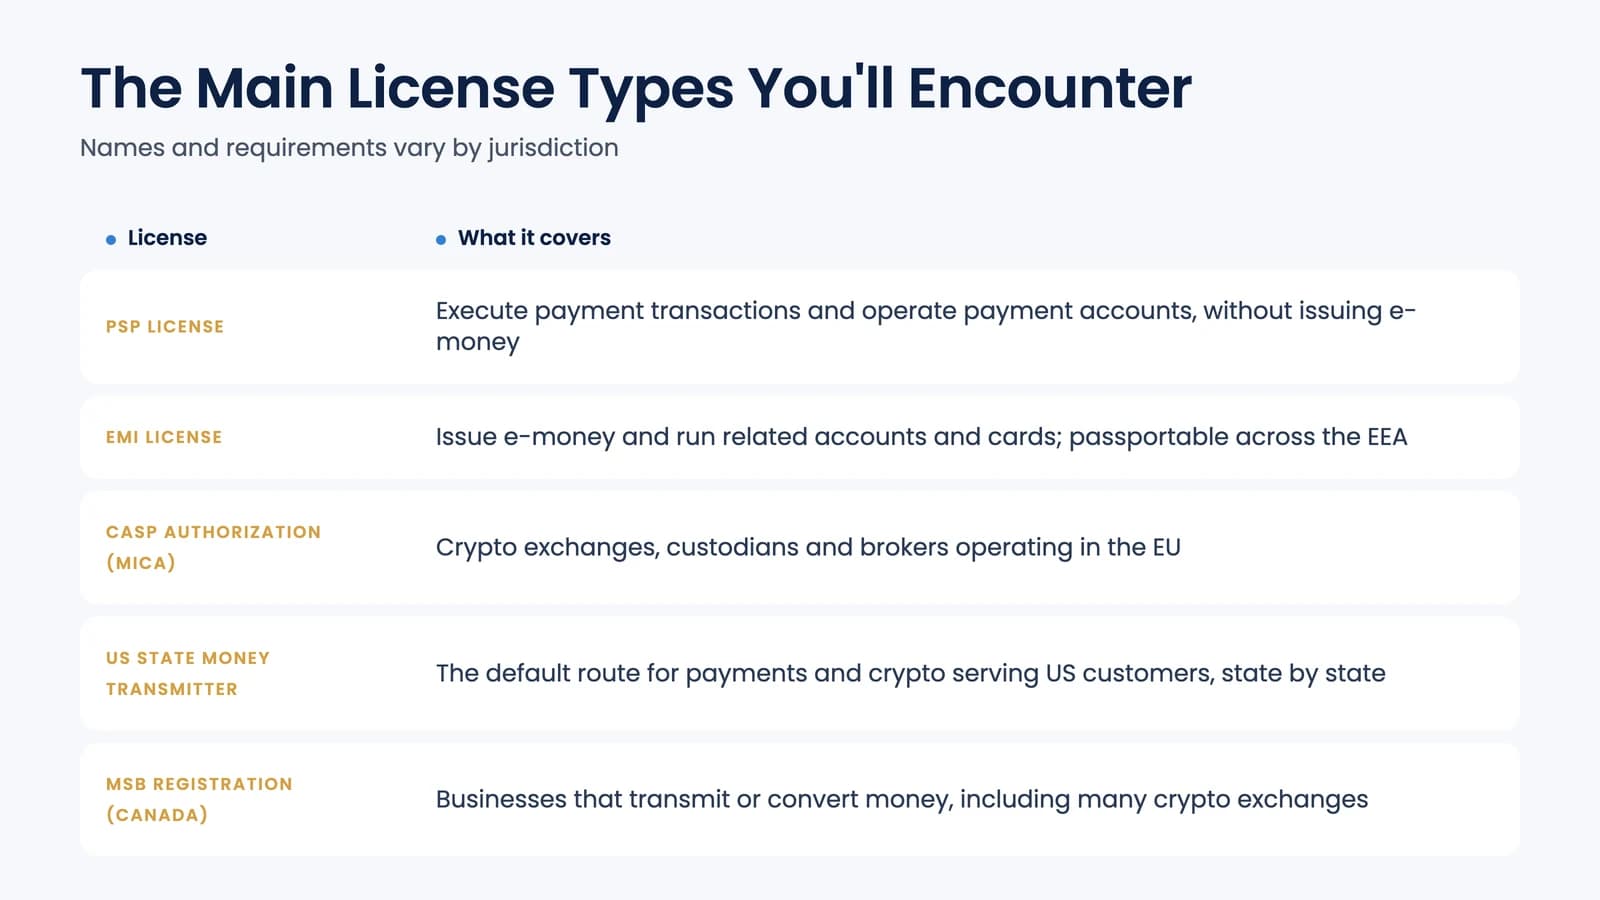
Names and exact requirements vary by jurisdiction, but most fintechs end up choosing among a short list of options.
- PSP license: lets you execute payment transactions and operate payment accounts, without issuing e-money yourself.
- EMI license: lets you issue e-money and run related accounts and cards. An EU EMI license can be passported across the EEA, which is why it's a popular choice for fintechs planning to operate in several European markets.
- CASP authorization under MiCA: required for crypto exchanges, custodians, and brokers operating in the EU. The regime has applied since 30 December 2024, and national transitional (grandfathering) periods for firms already operating ended no later than 1 July 2026, as ESMA confirmed.
- US state money-transmitter licenses: the default route for payments and crypto businesses serving US customers, typically needed state by state rather than under one federal license.
- Money Service Business (MSB) registration (Canada): needed for businesses that transmit or convert money, including many crypto exchanges.
What Regulators Actually Check
Beyond the paperwork, most license reviews come down to four areas:
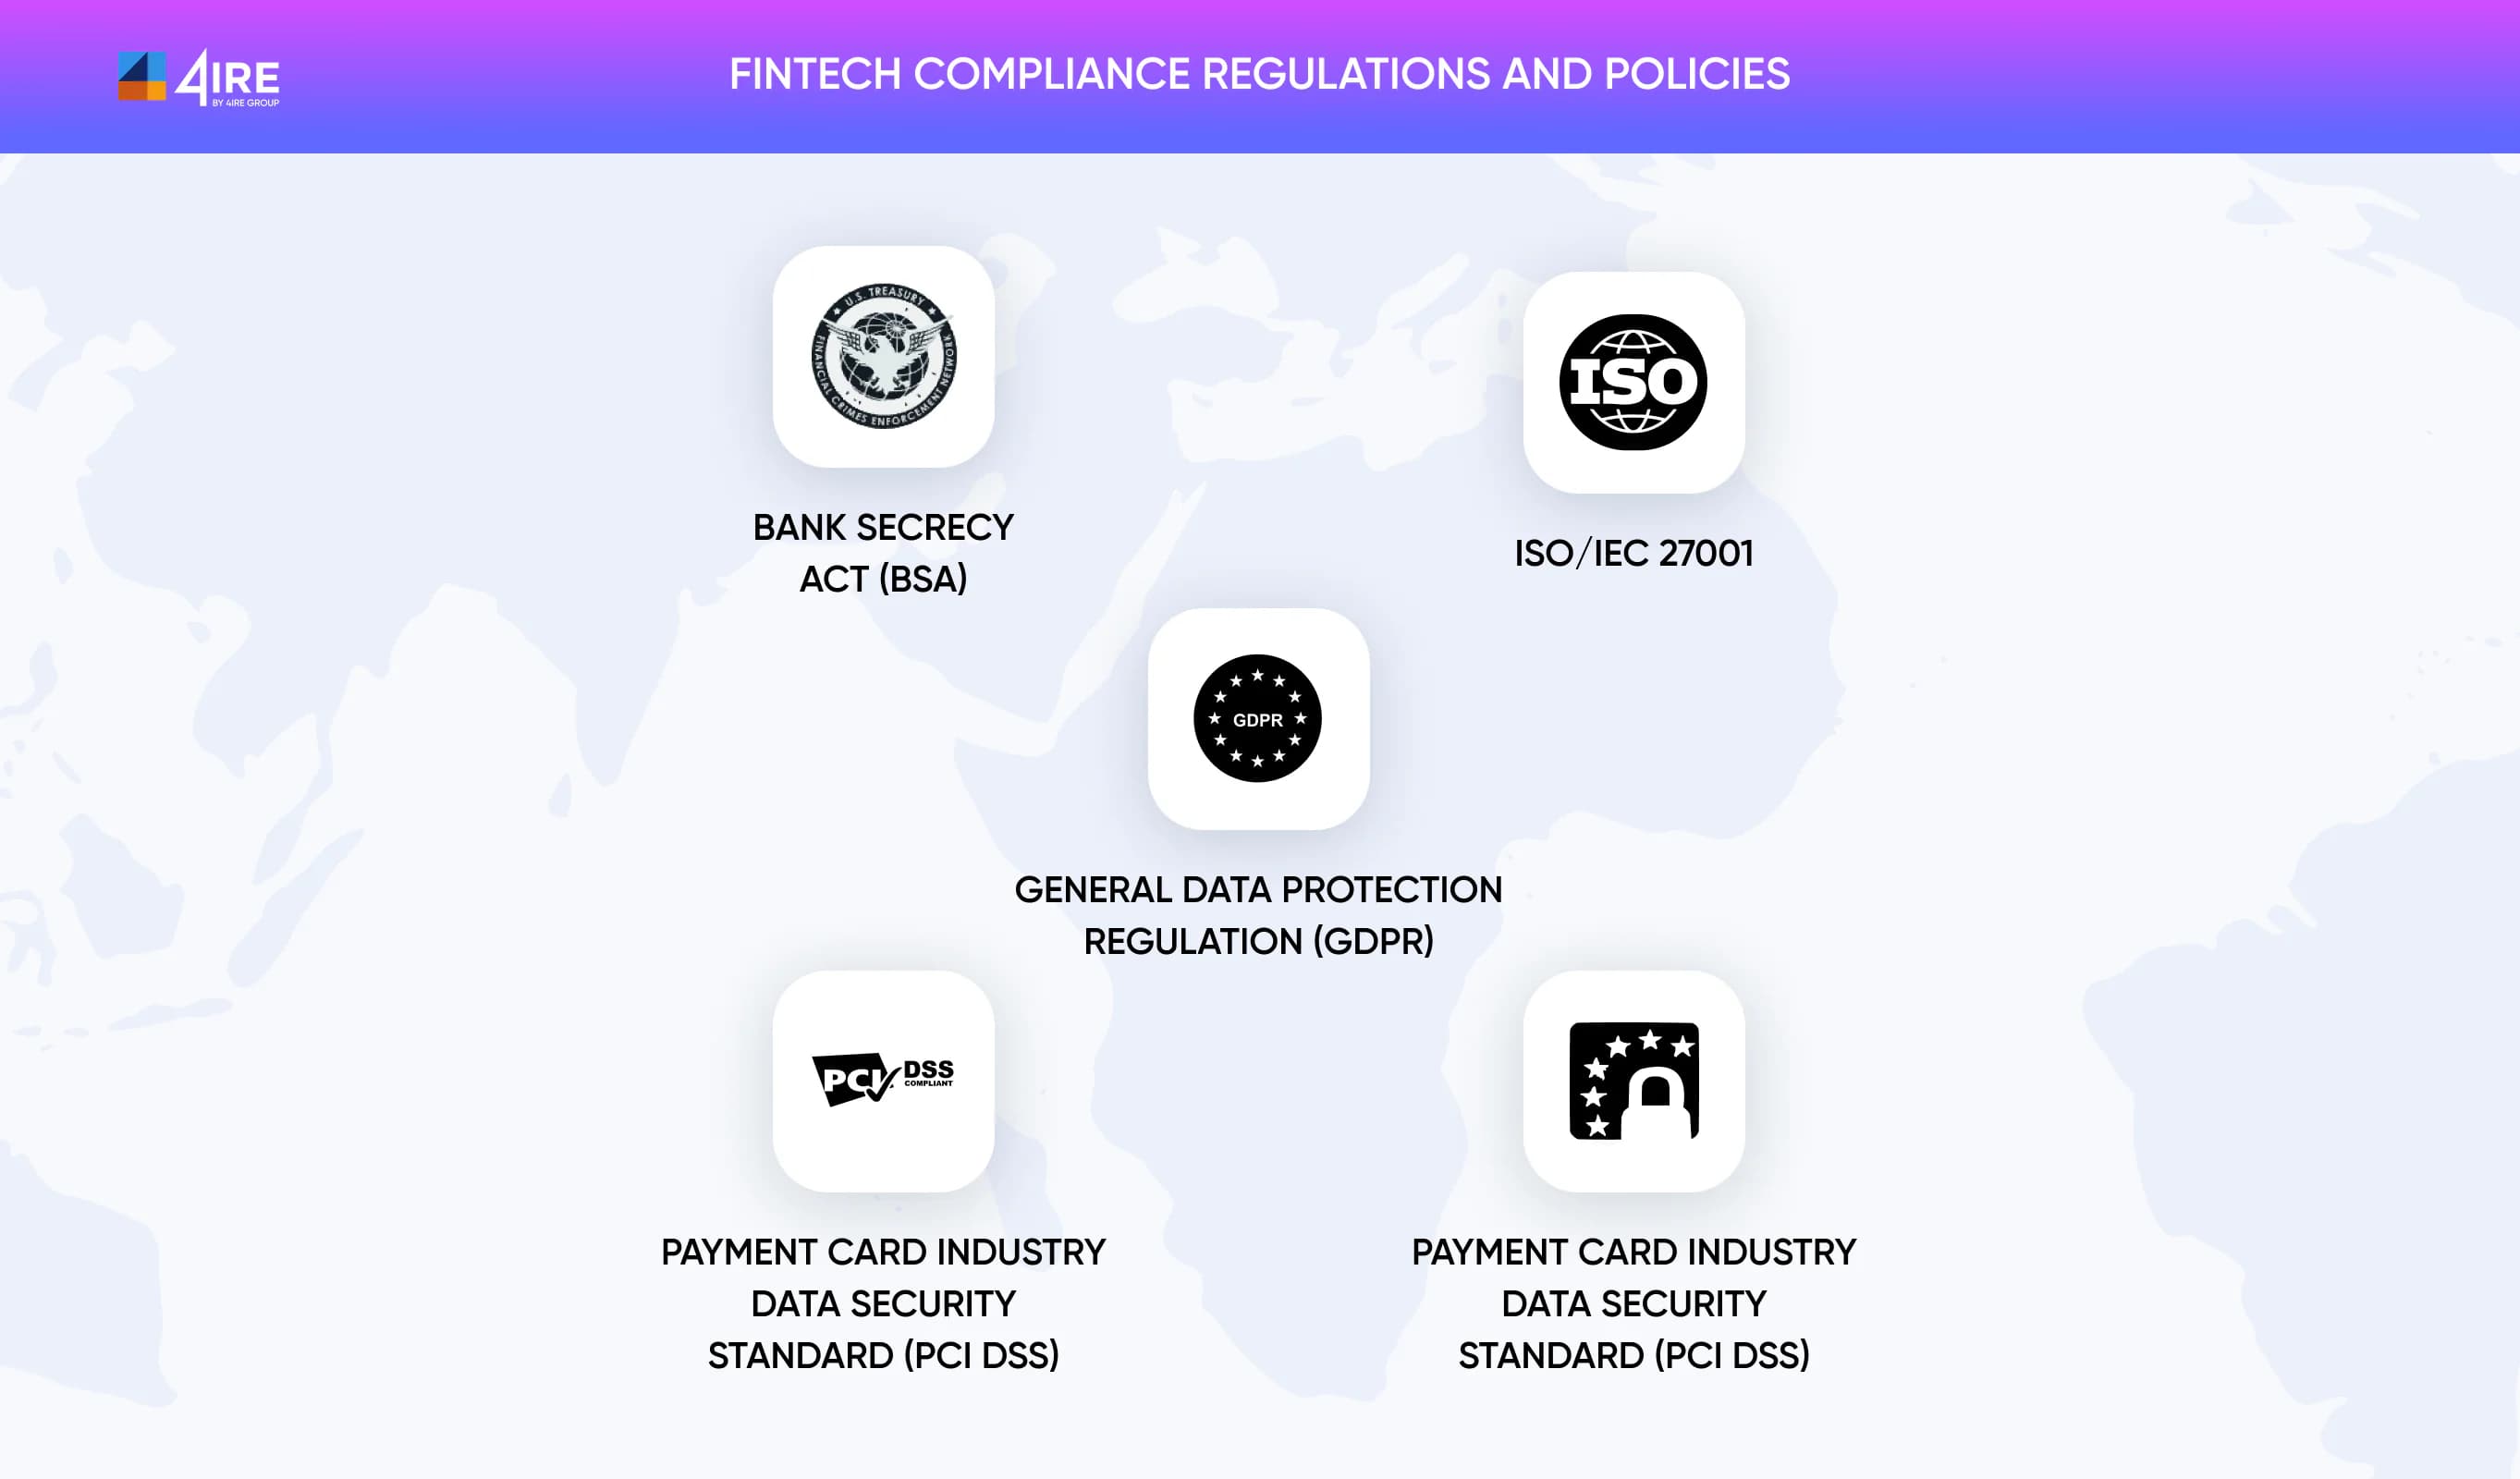
- Capital adequacy. Requirements are often tiered: an EMI, for example, may need capital equal to a percentage of its outstanding e-money float, on top of a fixed minimum.
- AML and KYC. A written anti-money-laundering policy addressed to your actual customer base and transaction patterns, not a generic template, plus evidence you can run it: onboarding checks, sanctions screening, and transaction monitoring.
- Data protection. EU fintechs handling personal data need GDPR-compliant processes, including data protection impact assessments. GDPR fines run up to €10 million or 2% of global annual turnover for the lower tier of infringements, and up to €20 million or 4% for the higher tier, whichever is greater.
- Operational resilience and security. Regulators increasingly want evidence of cybersecurity controls, such as ISO 27001 certification, and, for many EU financial entities, compliance with DORA's ICT risk-management and incident-reporting rules, which have applied since 17 January 2025.
How Long It Takes, and What It Actually Costs
There's no honest single number for timeline or cost, because both depend heavily on the license type, the jurisdiction, and how mature your compliance function already is. A partner-bank or agent arrangement can let you launch in weeks, because you rely on someone else's license. An own-account EMI or CASP authorization typically takes several months of preparation and regulatory review; a full banking license can take well over a year. Legal and compliance costs scale the same way: they depend on jurisdiction complexity and whether you build the compliance function in-house or bring in outside counsel. The most reliable way to get a real estimate is a scoped legal and compliance review of your specific business model and target markets, run before you commit to a launch date.
How 4IRE Can Help
4IRE builds the technology side of financial software so that it matches what you'll actually put in front of a regulator: KYC and AML flows built into onboarding and transactions, not bolted on before launch, and audit logs and reconciliation reports the ledger produces on its own. For crypto-facing products, our blockchain consulting and crypto wallet development work is built around the custody and key-management controls that MiCA and equivalent regimes expect. If you're scoping a licensed product, especially a neobank or wider fintech launch, our guide for fintech startups covers the rest of the launch checklist alongside licensing. Talk to us about your business model and target markets, and we'll help you find the right consultants to lead the licensing process while we build the product around it.
FAQ
Only if it touches customer money directly. Some business models plug into a licensed partner bank or banking-as-a-service provider and never hold their own license, though they still take on due diligence and integration obligations. Any business that issues e-money, executes payment transactions, offers crypto-asset services, or extends credit on its own account needs its own license or registration.
A PSP license lets you execute payment transactions and operate payment accounts. An EMI license covers that plus the ability to issue e-money balances yourself, which is what most card and multi-currency account products need.
It depends on whether you provide crypto-asset services yourself. If you exchange, custody, or broker crypto for clients in the EU, you need CASP authorization under MiCA. If you route payments through a licensed processor and never hold crypto on your own balance sheet, that processor carries the licensing burden instead.
No. There's no global fintech license. An EU EMI or CASP authorization can be passported across the EEA, which covers a large market with one application, but the US, UK, and most other jurisdictions require their own separate license or registration.
It ranges from a few weeks for a partner-bank arrangement to well over a year for a full banking license, with an own-account EMI or CASP authorization usually falling somewhere in between. A scoped legal review of your business model and target jurisdictions is the most reliable way to get a realistic timeline.