

 Cryptocurrency

A stablecoin is easy to deploy and hard to operate. The token contract takes days; the infrastructure that keeps supply matched to reserves on every chain, moves tokens between networks and satisfies regulators takes months. This guide is written for CTOs and technical leads who have to design that system.
The market is large enough to justify the effort. As of 28 September 2026, the supply of US dollar stablecoins stood at about $313 billion, according to DefiLlama. Ethereum carries roughly $146 billion of it and Tron about $94 billion, followed by Solana, BNB Chain, Hyperliquid and Base. The largest tokens live on dozens of networks at once, so multi-chain is now the default operating model for a serious issuer.
How a stablecoin works: minting, redemption and the peg
Every reserve-backed stablecoin runs on the same loop, whatever chain it lives on.
- Minting. An approved customer deposits collateral: fiat in a bank or custodian account for a fiat-backed coin, crypto locked in a smart contract for a crypto-collateralised one. Once the deposit is confirmed, the issuer mints the same value of tokens to the customer's wallet.
- Redemption. The holder returns tokens, the contract burns them, and the issuer releases the matching collateral. Burning on redemption is what keeps circulating supply from exceeding reserves.
- Peg maintenance. If the market price drifts below par, arbitrageurs buy cheap tokens and redeem them; above par, they mint and sell. The peg is only as strong as redemption access and reserve quality.
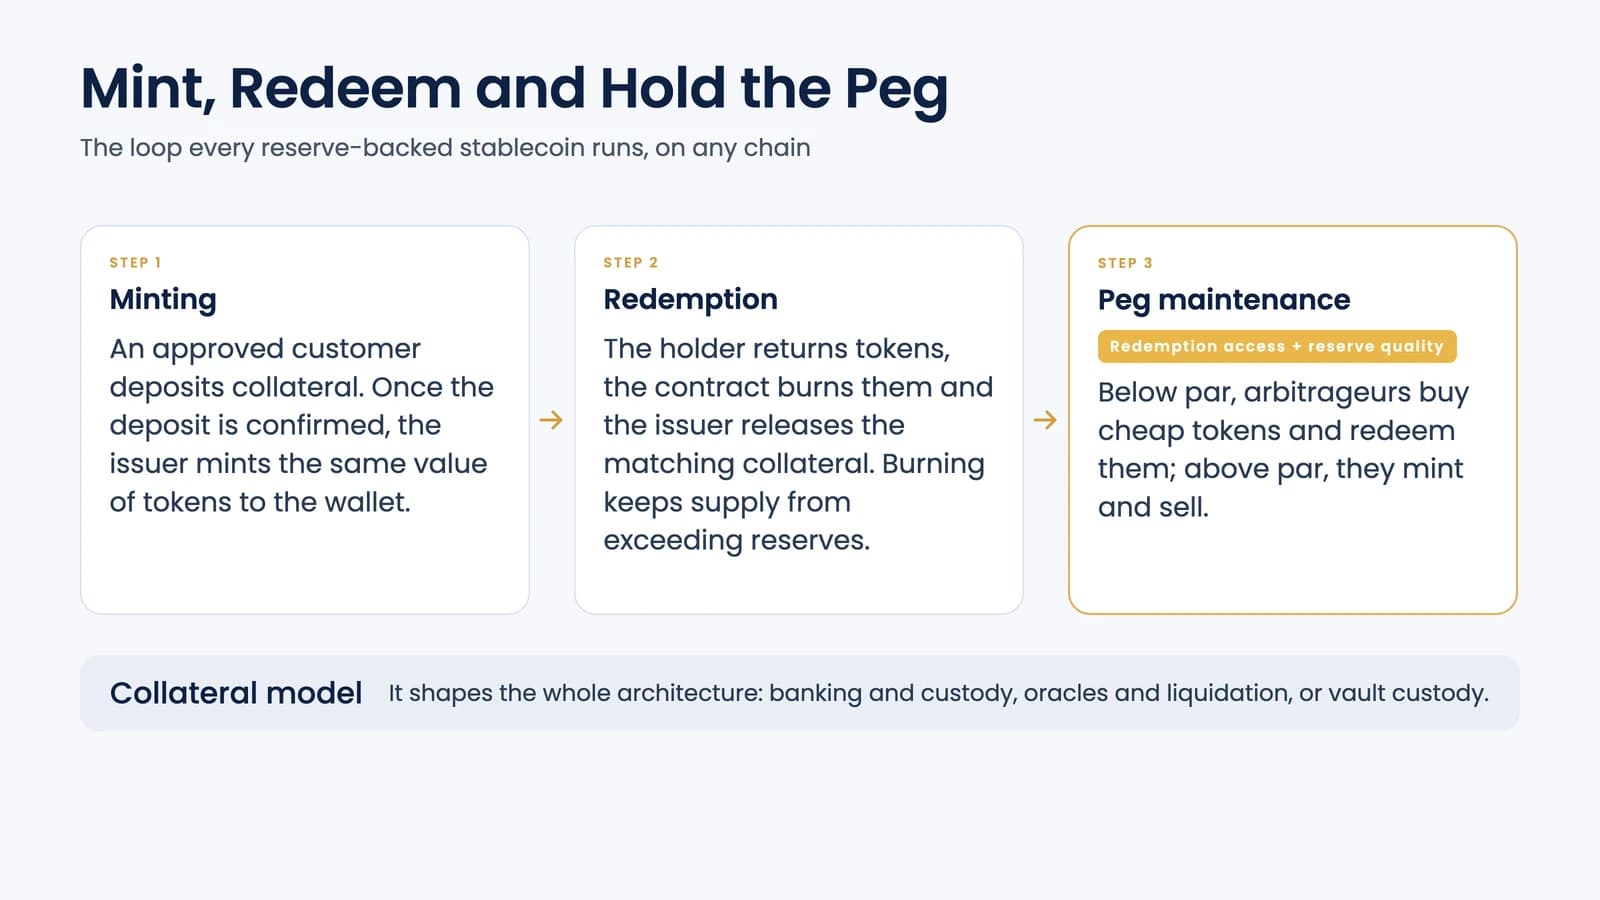
The collateral model shapes the whole architecture. Fiat-backed coins such as USDC, USDT and Circle's euro token EURC need banking, custody and attestation pipelines. Crypto-collateralised coins such as DAI and USDS need oracles, liquidation engines and overcollateralisation rules. Commodity-backed tokens such as PAXG and XAUT need vault custody and bar-level audits. Synthetic designs such as Ethena's USDe add derivatives venues and funding-rate risk. Our overview of stablecoin types and regulation compares them in more detail.
Cross-chain design: burn-and-mint instead of wrapped tokens
The first generation of multi-chain stablecoins relied on lock-and-mint bridges: the canonical token was locked in a bridge contract on one chain and a wrapped copy was minted on another. That created large escrow balances that attracted attackers, several incompatible versions of "the same" token and supply that was hard to reconcile against reserves.
Current designs move the supply itself:
- Native burn-and-mint. Circle's Cross-Chain Transfer Protocol (CCTP) burns USDC on the source chain, has Circle's attestation service confirm the burn and mints native USDC on the destination. There is no liquidity pool to drain, and every chain holds the same canonical asset.
- Omnichain token standards. USDT0 uses LayerZero's OFT standard: USDT is locked in one adapter contract on Ethereum and USDT0 is minted on other chains, so there is a single locked balance and one supply record instead of a separate wrapped token per bridge. Wormhole's Native Token Transfers and Chainlink CCIP offer comparable frameworks for issuers that want to control their own deployment.
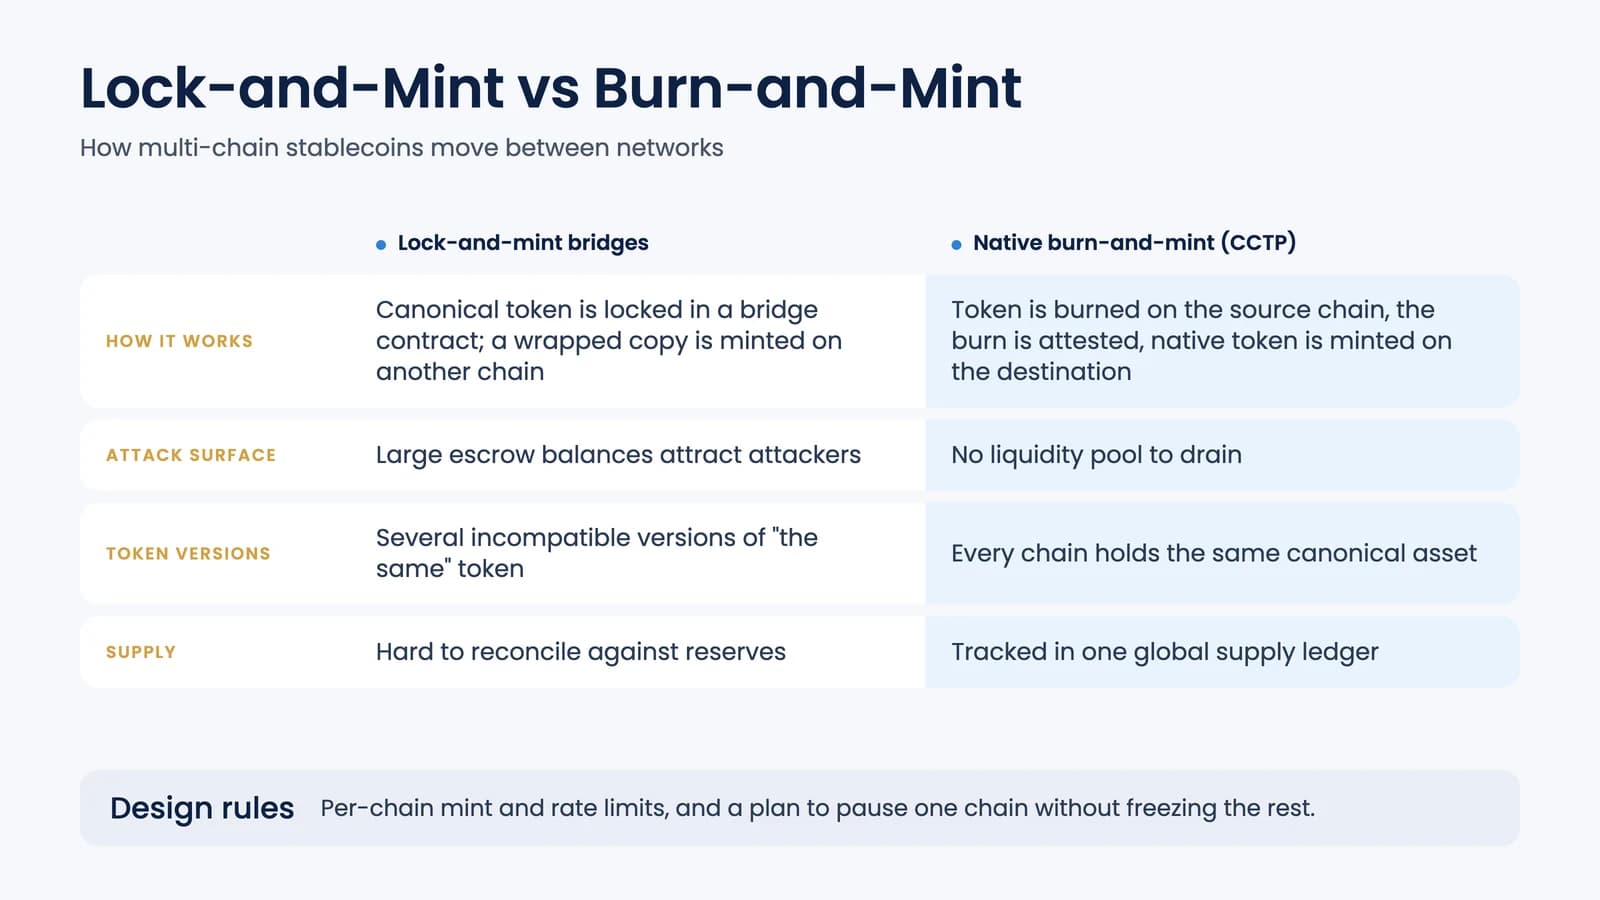
The architectural rules are the same for any messaging layer. Keep a global supply ledger that records mints and burns on every chain in one place. Set per-chain mint limits and rate limits, so a compromised route cannot inflate supply without bound. And plan how you will pause a single chain without freezing the rest. Our cross-chain development team treats the bridge layer as the highest-risk component of the system.
Proof of reserves, audits and reconciliation
A credible issuer publishes three kinds of evidence:
- Reserve attestations. Independent accountants confirm, usually monthly, that reserves at least equal circulating supply and describe what the reserves hold.
- On-chain supply data. Indexers sum the supply across all chains, net of tokens held in bridge contracts, so anyone can check the figure used in the attestation.
- Security audits. Every contract that can mint, burn, pause or upgrade needs an independent smart contract audit, repeated after significant changes.
Multi-chain operation makes reconciliation the hard part. Tokens are minted and burned on several networks in near real time, while the reserve sits in a small number of bank and custody accounts. Run automated supply-to-reserve reconciliation continuously, alert on any mismatch, and publish the data in a form that auditors and users can check independently.
Security and operational controls
Most stablecoin failures come from a small set of causes: an algorithmic peg that breaks under stress, reserves that are misreported or lost, a contract bug that allows unauthorised minting, a flaw in burn logic that leaves supply out of sync, or an insider abusing privileged keys. The controls we recommend map directly to them:
- Multi-signature approval (for example, a multisig wallet with separate signer roles) for minting permissions, treasury moves, contract upgrades and emergency pauses, so no single person or key can act alone.
- Hardened key management. Privileged keys belong in HSMs or MPC wallets with role separation and tested recovery procedures.
- Timelocks on upgrades and parameter changes, which give the team and the market time to spot and stop a malicious change.
- Backend-driven issuance. Mints are triggered by the reserve system after the deposit settles, never by a manual transaction.
- Continuous monitoring of peg, supply, bridge flows and sanctioned addresses, with automated alerts and a documented incident playbook.
Regulation: what the architecture has to support
- United States. The GENIUS Act, signed on 18 July 2025, requires payment stablecoin issuers to hold at least 1:1 reserves in cash, deposits, short-dated Treasuries and similar assets, publish monthly reserve reports and pay no interest to holders. It takes effect by 18 January 2027 at the latest; implementing rules were still being finalised in September 2026.
- European Union. Under MiCA, single-currency tokens are e-money tokens and basket-referenced tokens are asset-referenced tokens. Stablecoin rules have applied since 30 June 2024, and issuers need authorisation, a white paper and reserve and governance controls.
- United Kingdom. The FCA published final rules for the new cryptoasset regime, including stablecoin issuance and custody, on 30 June 2026. The application window opened on 30 September 2026 and closes on 28 February 2027; the regime is expected to take effect on 25 October 2027.
- Hong Kong and the UAE. Hong Kong's Stablecoins Ordinance has been in force since 1 August 2025, and the first issuer licences were granted in April 2026. The UAE Central Bank's Payment Token Services Regulation governs dirham-backed and foreign payment tokens used in the UAE.
For engineering, this means freeze and pause functions, address screening, jurisdiction-aware distribution, reserve reporting and audit trails need to be designed in from the start. Banks should also weigh stablecoins vs deposit tokens before choosing a model.
Technology stack
- Contracts. Solidity for EVM chains, Rust for Solana. ERC-20 with EIP-2612 permit, role-based access control and a well-understood upgradeable proxy pattern.
- Development and testing. Foundry or Hardhat, local forks and Tenderly for simulation.
- Verification. Slither for static analysis, Echidna or Foundry for fuzzing, and formal verification (Certora or similar) for supply invariants.
- Cross-chain and data. CCTP, OFT, NTT or CCIP for transfers; Chainlink or redundant oracle feeds where prices matter.
- Reserves and compliance. Supply indexers, attestation pipelines, and blockchain analytics such as Chainalysis, TRM Labs or Elliptic for screening and investigations.
What it costs and how long it takes
The figures below are 4IRE's commercial estimates from our own projects, not market benchmarks:
- Initial build of a fiat-backed stablecoin: from about $100,000 for contracts, issuance and redemption backend, APIs, an admin interface and the first security audit. Collateral, licensing and legal work come on top.
- Running costs: typically $10,000–$50,000 a year for attestations, proof of reserves, repeat audits, monitoring and maintenance.
- Team location: in our experience a comparable scope costs roughly $80,000–$200,000 with a Central and Eastern European team and $200,000–$500,000 or more with a US-based team.
A short discovery phase is the cheapest way to control that budget: it fixes the collateral model, chains, bridge design and compliance scope before any code is written. Licensing, banking and custody partners are usually on the critical path, not the smart contracts.
A delivery sequence that works
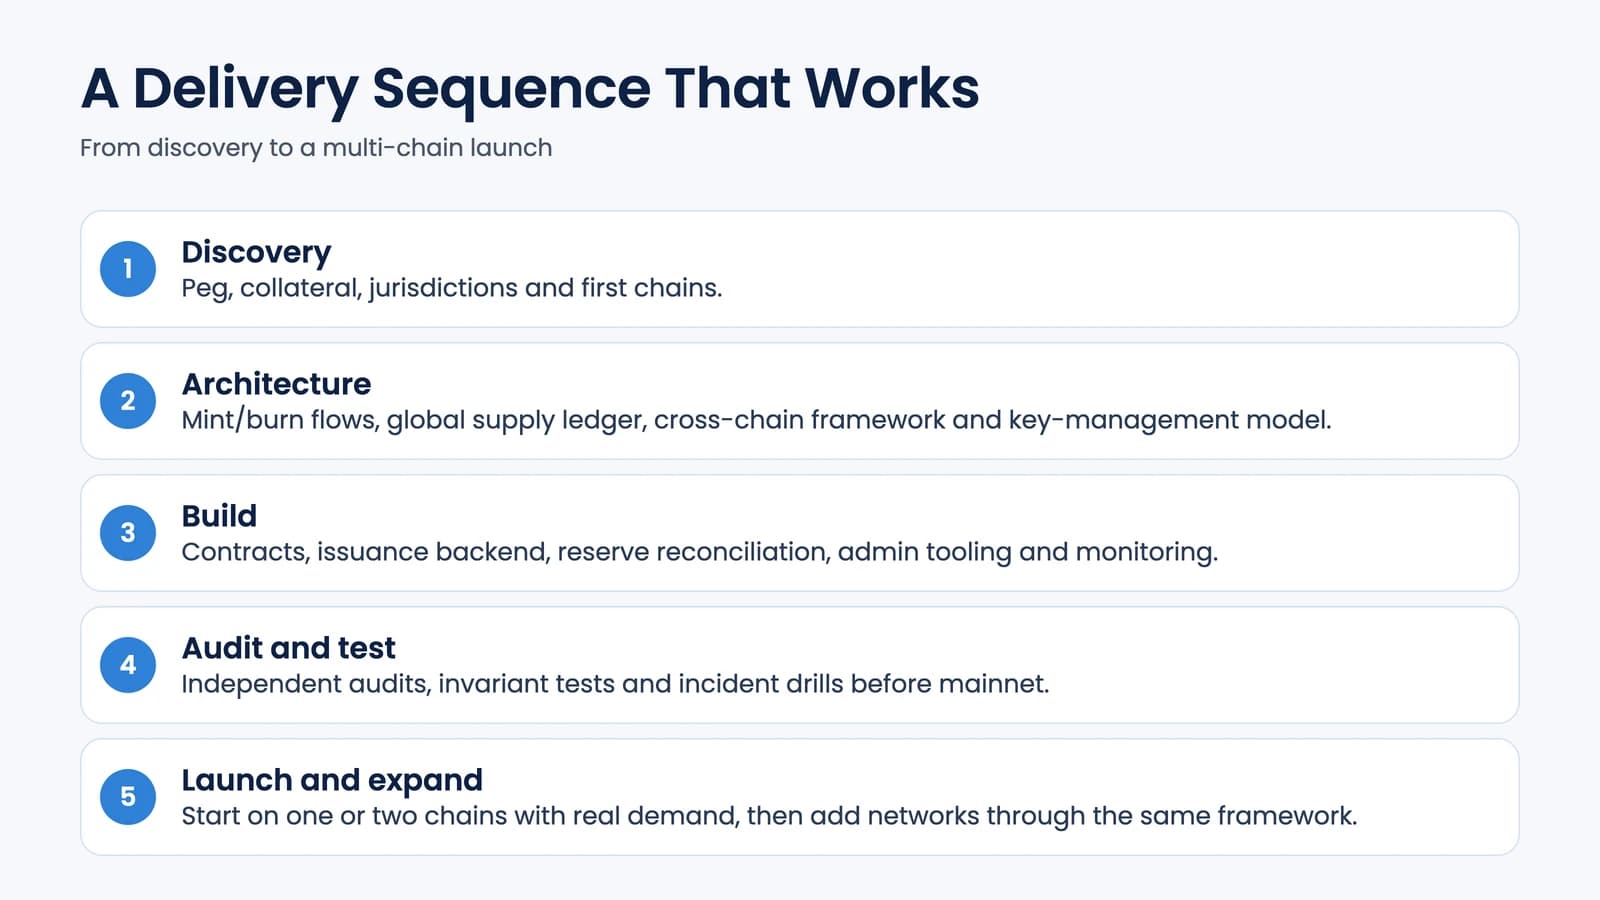
- Discovery. Peg, collateral, jurisdictions and first chains.
- Architecture. Design the mint/burn flows, global supply ledger, cross-chain framework and key-management model.
- Build. Contracts, issuance backend, reserve reconciliation, admin tooling and monitoring.
- Audit and test. Independent audits, invariant tests and incident drills before mainnet.
- Launch and expand. Start on one or two chains with real demand, then add networks through the same burn-and-mint framework.
For the contract-level details of a first deployment, see our walkthrough on how to create a stablecoin on Ethereum.
Conclusion
Multi-chain stablecoin infrastructure is about keeping one number honest everywhere: supply on every chain must match the reserve behind it, under any failure. Teams that design supply accounting, cross-chain transfers, key controls and regulatory reporting as one system launch faster and hold up better in audits. If you are planning an issuance or a stablecoin payment product, our cryptocurrency development team can help you scope it.
FAQ on stablecoin infrastructure
It is the set of contracts, backend services and controls that let one stablecoin be issued and redeemed on several blockchains while total supply stays matched to a single reserve. It covers minting and burning, cross-chain transfers, reserve reconciliation, key management and compliance tooling.
Generally, yes. Burn-and-mint frameworks such as Circle's CCTP move native supply between chains instead of holding large locked balances in a bridge contract, which removes a common attack target and avoids several competing versions of the same token. The messaging layer and mint limits still need careful design and audits.
By 4IRE's estimates, the technical build starts at about $100,000, with $10,000–$50,000 a year in running costs for attestations, audits and maintenance. Licensing, legal structuring, banking and custody are separate and often cost as much as the technology.
It depends on where you serve users. The main regimes are the US GENIUS Act (effective by January 2027), MiCA in the EU, the UK's FCA regime (from October 2027), Hong Kong's Stablecoins Ordinance and the UAE Central Bank's payment token rules.
Custom development gives full control over contracts, keys and compliance logic and suits regulated issuers. Pre-built modules shorten time to market for standard flows such as wallets and payments. Many teams combine the two: custom issuance and reserve logic, reused components around it.