

Most fintech startups that stall don't stall because the idea was weak. They stall because compliance, data protection, and trust-building were treated as launch-week tasks instead of product decisions made from day one. Financial products carry a regulatory and reputational weight that a typical consumer app doesn't, and the founders who plan for that early move faster later, not slower.
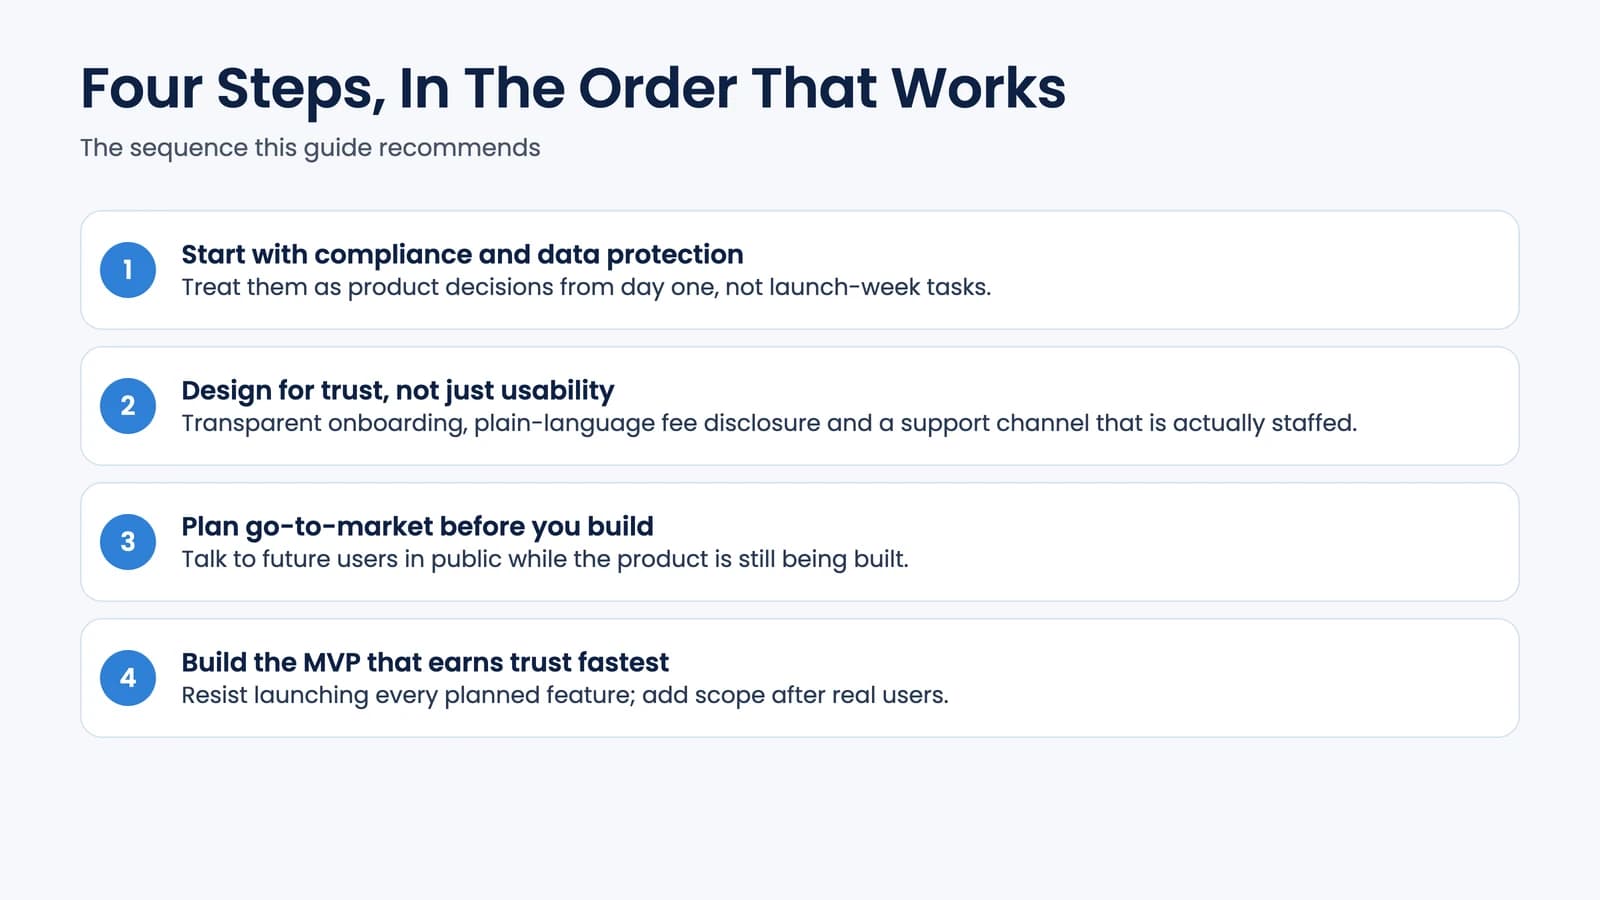
This guide walks through the sequence we see work in practice: get compliance and data protection right first, design the product around trust rather than just usability, and only then plan the go-to-market push. If you've already validated the idea and are deciding whether you need a license at all, read that alongside when your fintech needs licensing.
Start With Compliance, Not After It
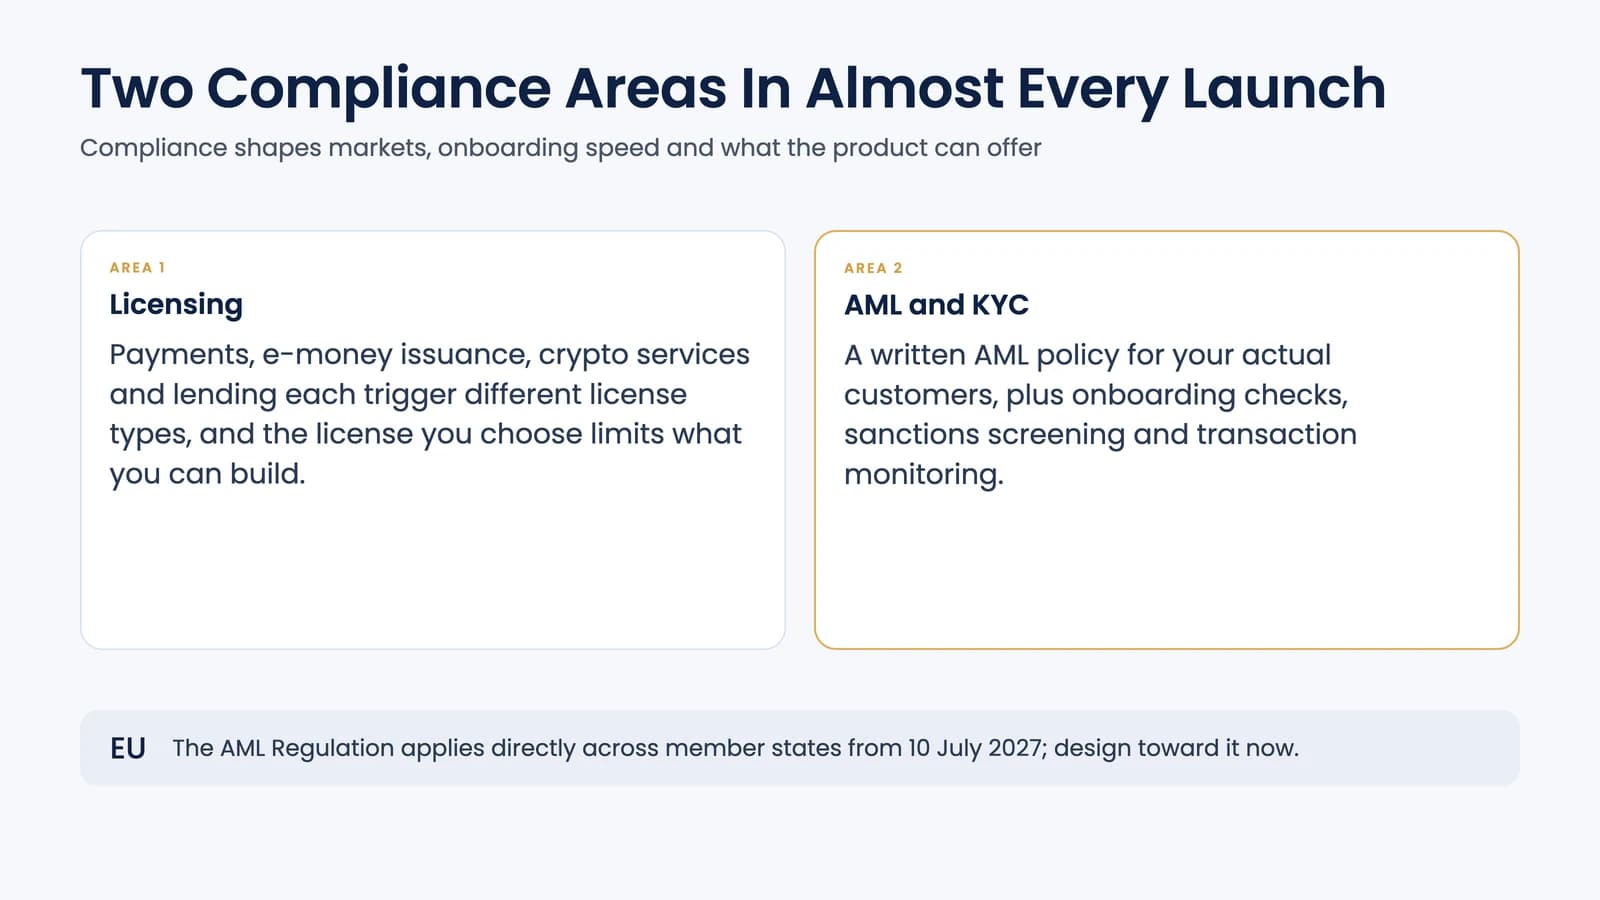
Legal compliance shapes which markets you can operate in, how fast you can onboard users, and what your product can actually offer, so it belongs in the same conversation as your feature roadmap. Two areas come up in almost every fintech launch:
- Licensing. Payments, e-money issuance, crypto services, and lending each trigger different license types, and the license you choose limits what you can build. Our guide on types of licenses for fintech and crypto breaks down PSP, EMI, and crypto-asset licenses in more detail.
- AML and KYC. A written AML policy addressed to your actual customer base and transaction patterns, not a template, plus the onboarding checks, sanctions screening, and transaction monitoring to back it up. In the EU, keep an eye on the incoming AML Regulation, which applies directly across all member states from 10 July 2027 and is worth designing toward now rather than retrofitting later.
Build a Data Protection Program Founders Actually Use
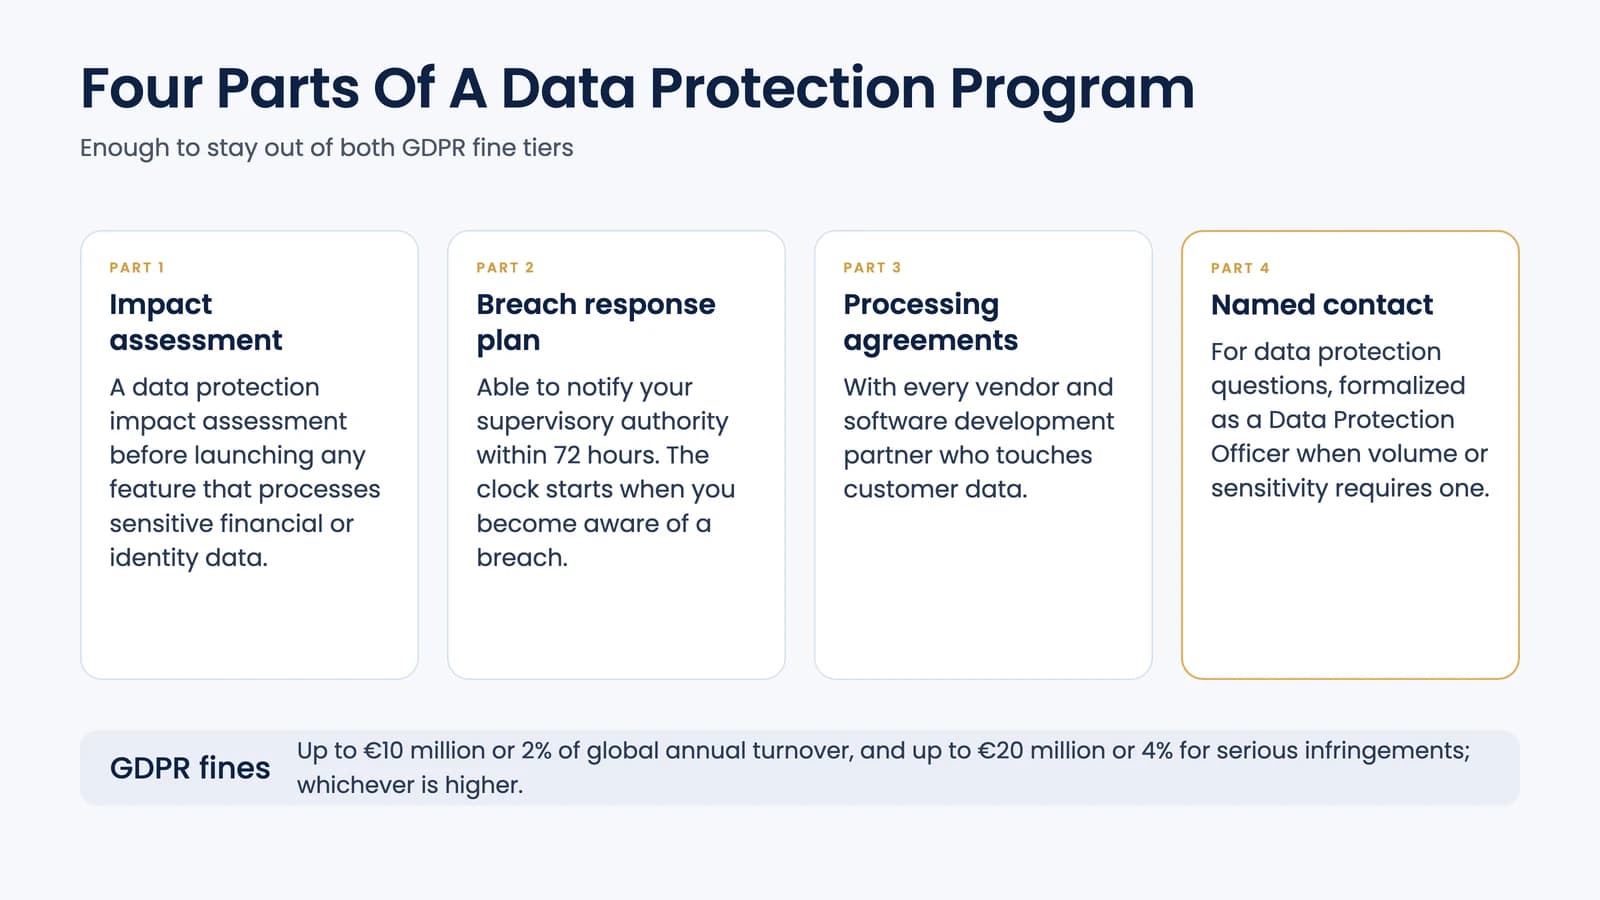
If you handle EU customer data, GDPR isn't optional paperwork. Fines run in two tiers: up to €10 million or 2% of global annual turnover for the lower tier, and up to €20 million or 4% for serious infringements involving core data-subject rights, whichever amount is higher in each case. The practical program that keeps you out of both tiers includes:
- A data protection impact assessment before you launch any feature that processes sensitive financial or identity data.
- A breach response plan that can notify your supervisory authority within 72 hours, because that clock starts the moment you become aware of a breach, not when you've finished investigating it.
- Data processing agreements with every vendor and software development partner who touches customer data, with clear responsibility for security at each stage.
- A named contact for data protection questions, formalized as a Data Protection Officer once your processing volume or sensitivity requires one.
Design for Trust, Not Just Usability
Fintech is a category where users need to trust you before they'll try you, which is a higher bar than most consumer software has to clear. A few product decisions do more for trust than visual polish: fast, transparent onboarding that explains why you're asking for each piece of identity information; upfront, plain-language fee disclosure with no surprise charges; and a support channel that's actually staffed, since a frozen account with no human to call is the fastest way to lose a financial-services customer for good. Test these flows with real users before launch, not just internally, because your team already trusts the product by default.
Plan Your Go-to-Market Before You Build
Don't assume users will show up once the app is live. Robinhood built demand for its zero-commission trading app for nearly a year before launch by publishing content for prospective users and building a visible waitlist, largely through word of mouth on Reddit, and converted that into a large first wave of signups at launch. You don't need the same channel or scale, but the principle holds: start talking to your future users, in public, while the product is still being built, so day one isn't the first time they hear from you.
Once you're live, referral programs tend to outperform paid acquisition in financial services, where trust transfers more easily from a friend's recommendation than from an ad. Keep the mechanics simple and the reward meaningful enough to act on, and make sure your compliance team has signed off on any cash or credit incentive before it ships.
Building the MVP
Whether you're building a lending product, a payments app, or a full mobile banking app, resist the urge to launch every feature you've planned. Ship the one product that earns trust fastest for your specific niche, get it in front of real users, and add scope from there. If lending is part of your roadmap, plan your credit scoring system alongside your MVP rather than bolting it on later, since it affects both your licensing needs and your underwriting architecture. And if the long-term plan is a full digital bank rather than a single product, our guide on how to start a neobank covers the additional licensing and core-platform decisions that come with that scope.
How 4IRE Can Help
4IRE works with fintech founders from idea validation through to launch: financial software development with compliance built into onboarding and transaction flows rather than added afterward, plus support finding legal and licensing consultants for your specific jurisdiction. Talk to us about your product, your target market, and your timeline, and we'll help you sequence the compliance, build, and launch work so none of it blocks the others.
FAQ
Whether your business model needs a license, and if so, which one. That decision shapes your target markets, your capital requirements, and how much of the product you can build before you need a licensed partner. Work it out before you commit to a full feature roadmap.
Any business processing personal data of people in the EU needs to comply, regardless of where the company itself is based. Fintech products handle identity and financial data by nature, which puts them squarely in scope, and the fines for serious infringements (up to €20 million or 4% of global turnover) make this one of the costlier areas to get wrong.
Most early-stage fintechs do, at least initially. Specialized fintech law firms and compliance consultants can move faster than building an in-house legal function from scratch, and many software development partners already have relationships with firms that focus specifically on payments and crypto regulation.
Before launch, not after. Building an audience, whether through content, a waitlist, or early access, while the product is still in development means you have a group of interested, informed users on day one instead of starting customer acquisition from zero at launch.